> ## Documentation Index
> Fetch the complete documentation index at: https://wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva.mintlify.site/llms.txt
> Use this file to discover all available pages before exploring further.

# Okta

> Setting up SSO with Okta

### Steps to set Okta as an OIDC identity provider

<Steps>
  <Step>
    Navigate to the Applications view within your Okta Administrator Dashboard.
  </Step>

  <Step>
    Click on **Create App Integration**.
  </Step>

  <Step>
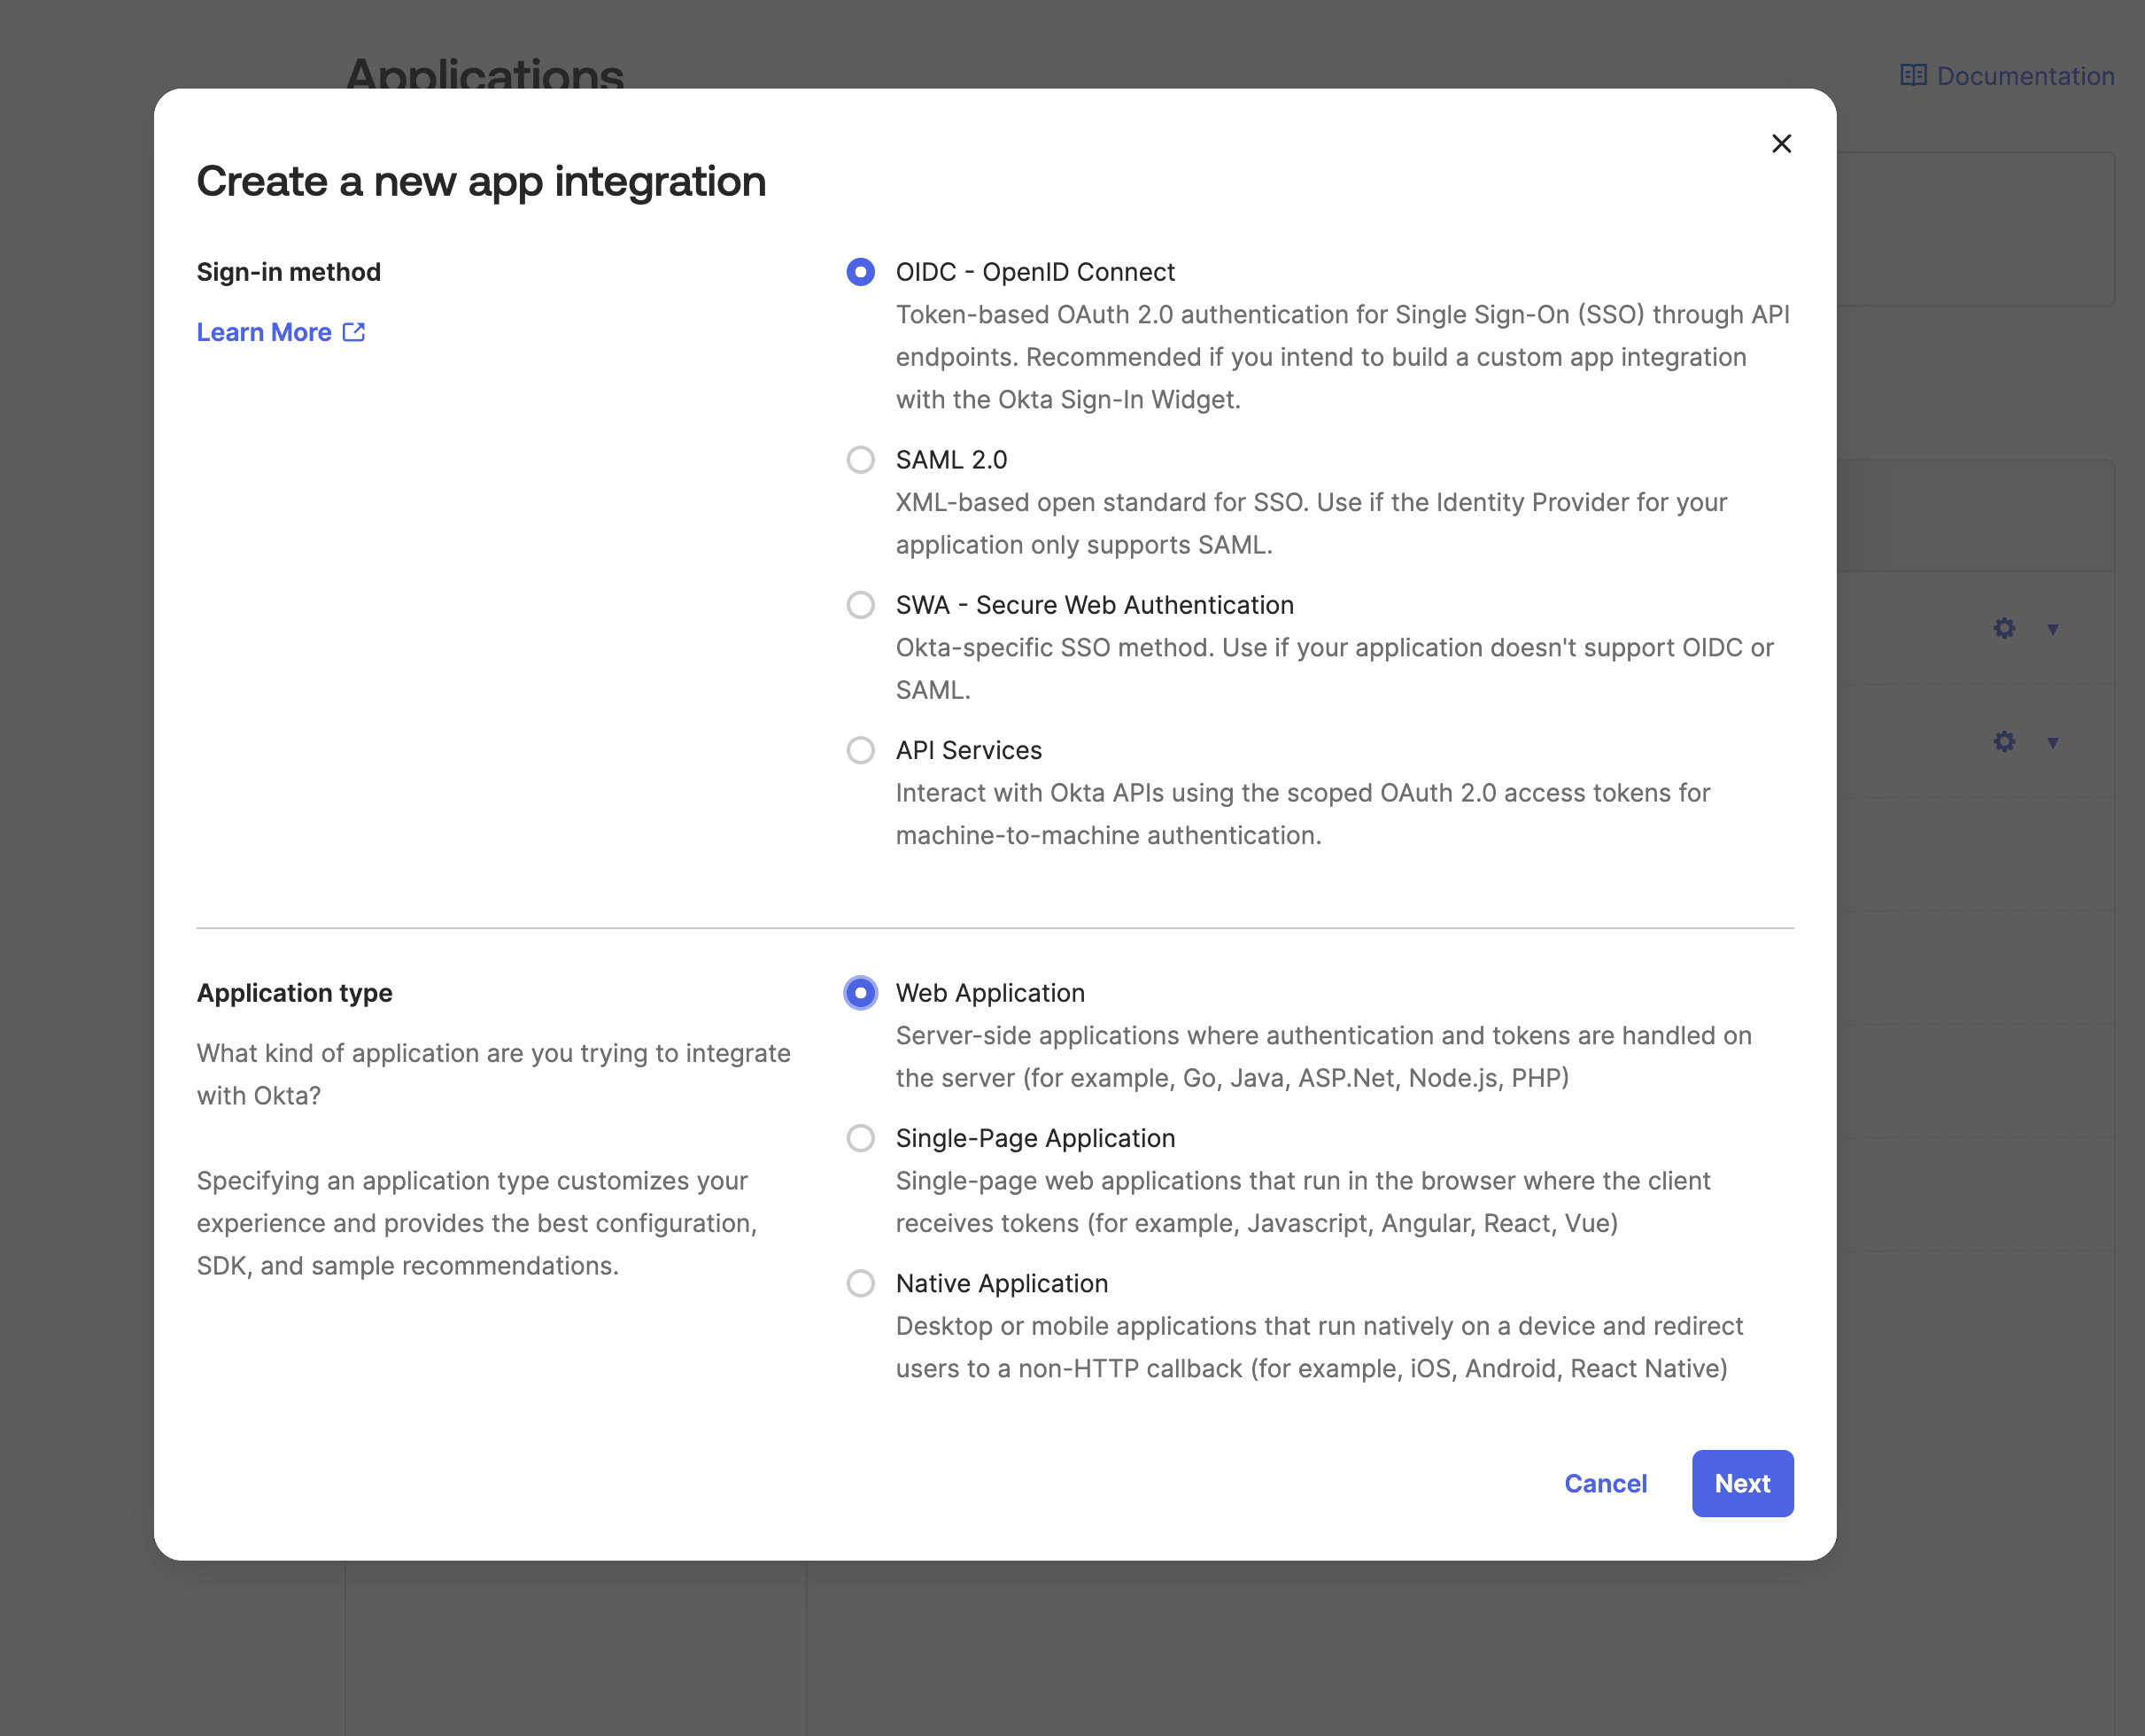
    A dialog appears, select **OIDC - OpenID Connect** as the sign-in method.
  </Step>

  <Step>
    For the application type, select **Web Application** and click on **Next**.
    <Frame>
      <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/create-new-app-integration-setup.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=024c91708dead49dda0d6fa806c14508" alt="Create new app integration page for selecting sign-in method and application type" title="Create new app integration setup" width="2422" height="1960" data-path="images/studio/sso/create-new-app-integration-setup.png" />
    </Frame>
  </Step>

  <Step>
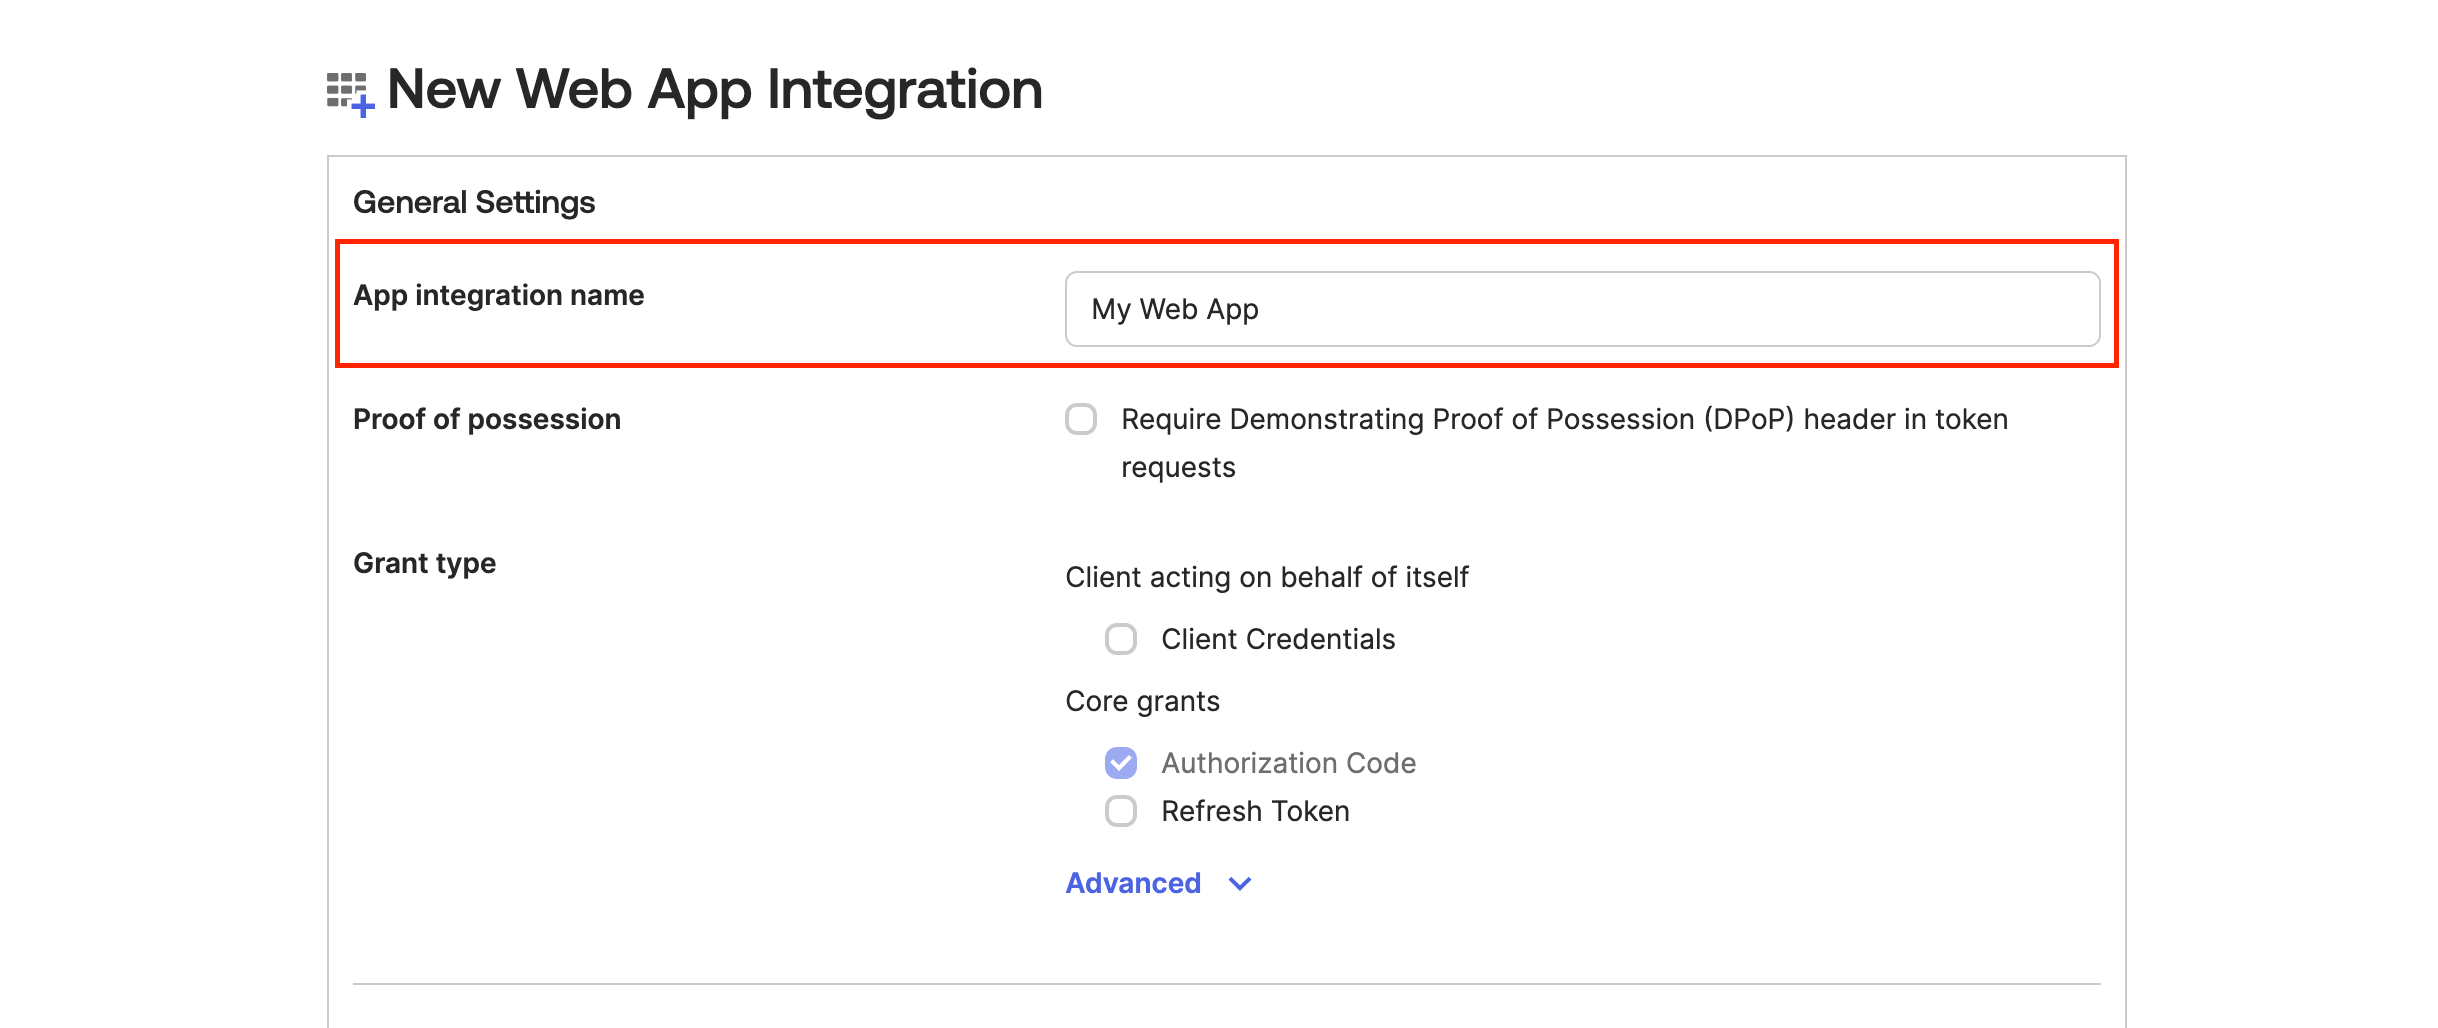
    Now give the app a name.

    <Frame>
      <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/app-integration-name-settings.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=e17a9534497072781981d8f0d2e77572" alt="Web app integration settings showing App integration name field set to My Web App" title="App integration name settings" width="2438" height="1028" data-path="images/studio/sso/app-integration-name-settings.png" />

      />
    </Frame>
  </Step>

  <Step>
    For **Grant Type,** keep the defaults.
  </Step>

  <Step>
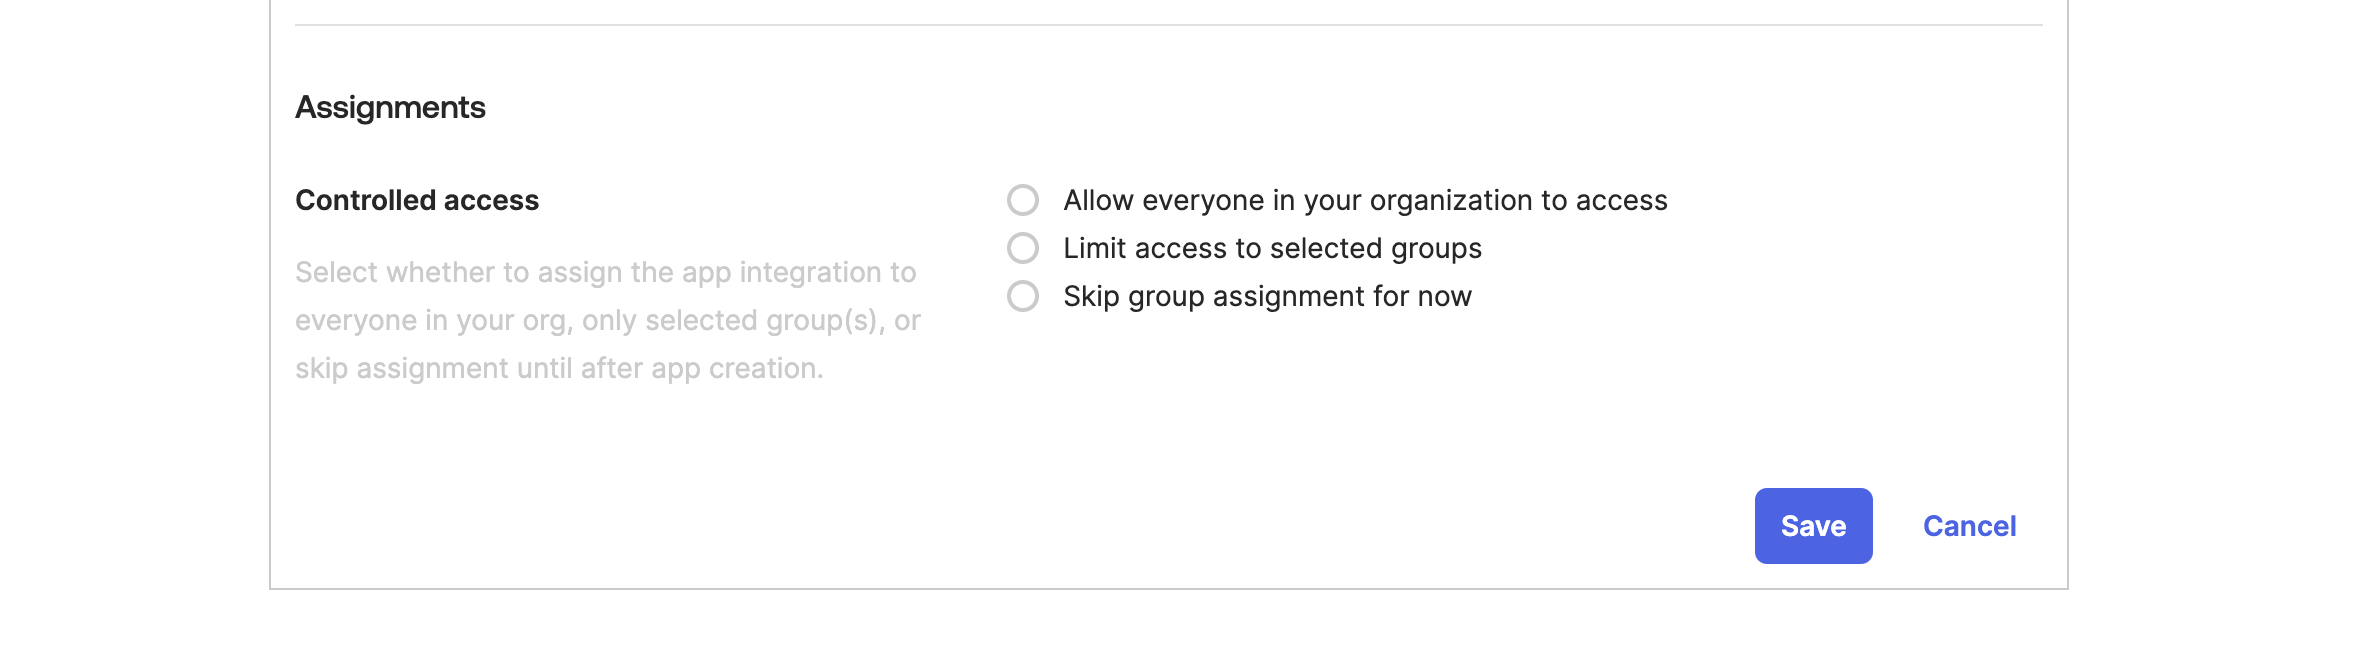
    Scroll down to the **Assignments** section and select one of the options based on your choice and then click on **Save.**
    <Frame>
      <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/assign-controlled-access-to-app.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=82c8a69637be85f2beeb445b98111eaf" alt="Cosmo Docs access assignment dialog with options for group or org-wide access" title="Assign controlled access to app" width="2356" height="652" data-path="images/studio/sso/assign-controlled-access-to-app.png" />

      />
    </Frame>
  </Step>

  <Step>
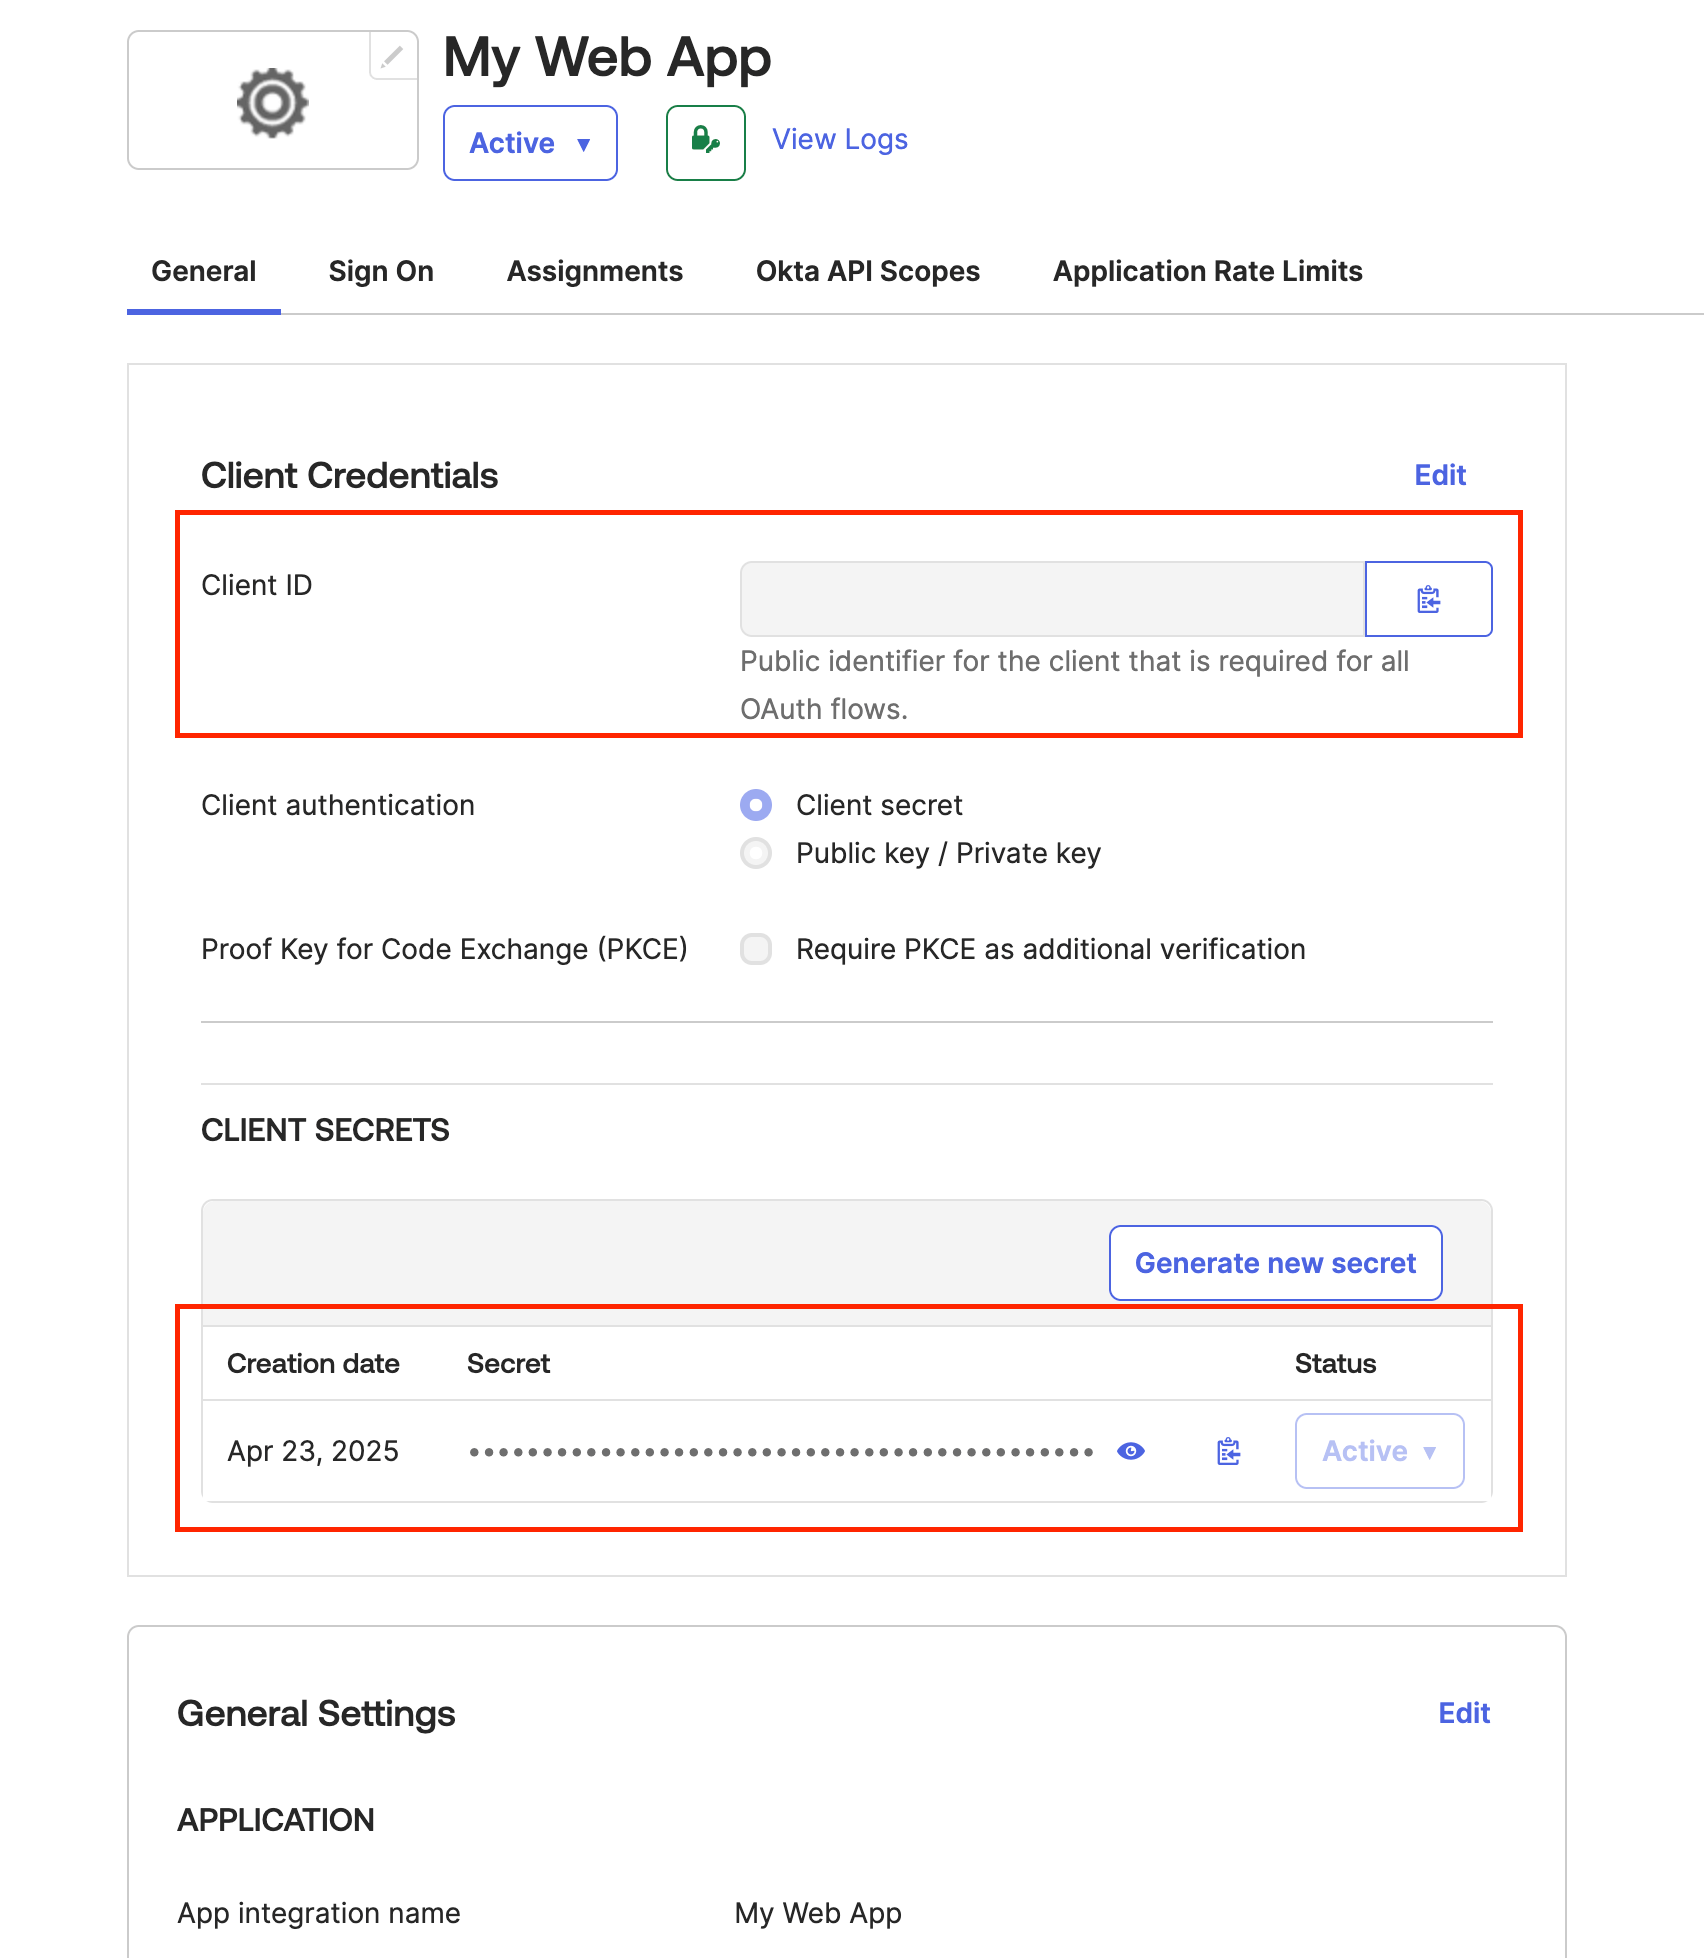
    Copy the **Client ID** and **Client Secret.**
    <Frame>
      <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/client-credentials-editing-view.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=3f2ce298b9e1ba1d6c1e72f45893acbd" alt="Client Credentials section editing client ID for OAuth flows" title="Client credentials editing view" width="1704" height="1958" data-path="images/studio/sso/client-credentials-editing-view.png" />
    </Frame>
  </Step>

  <Step>
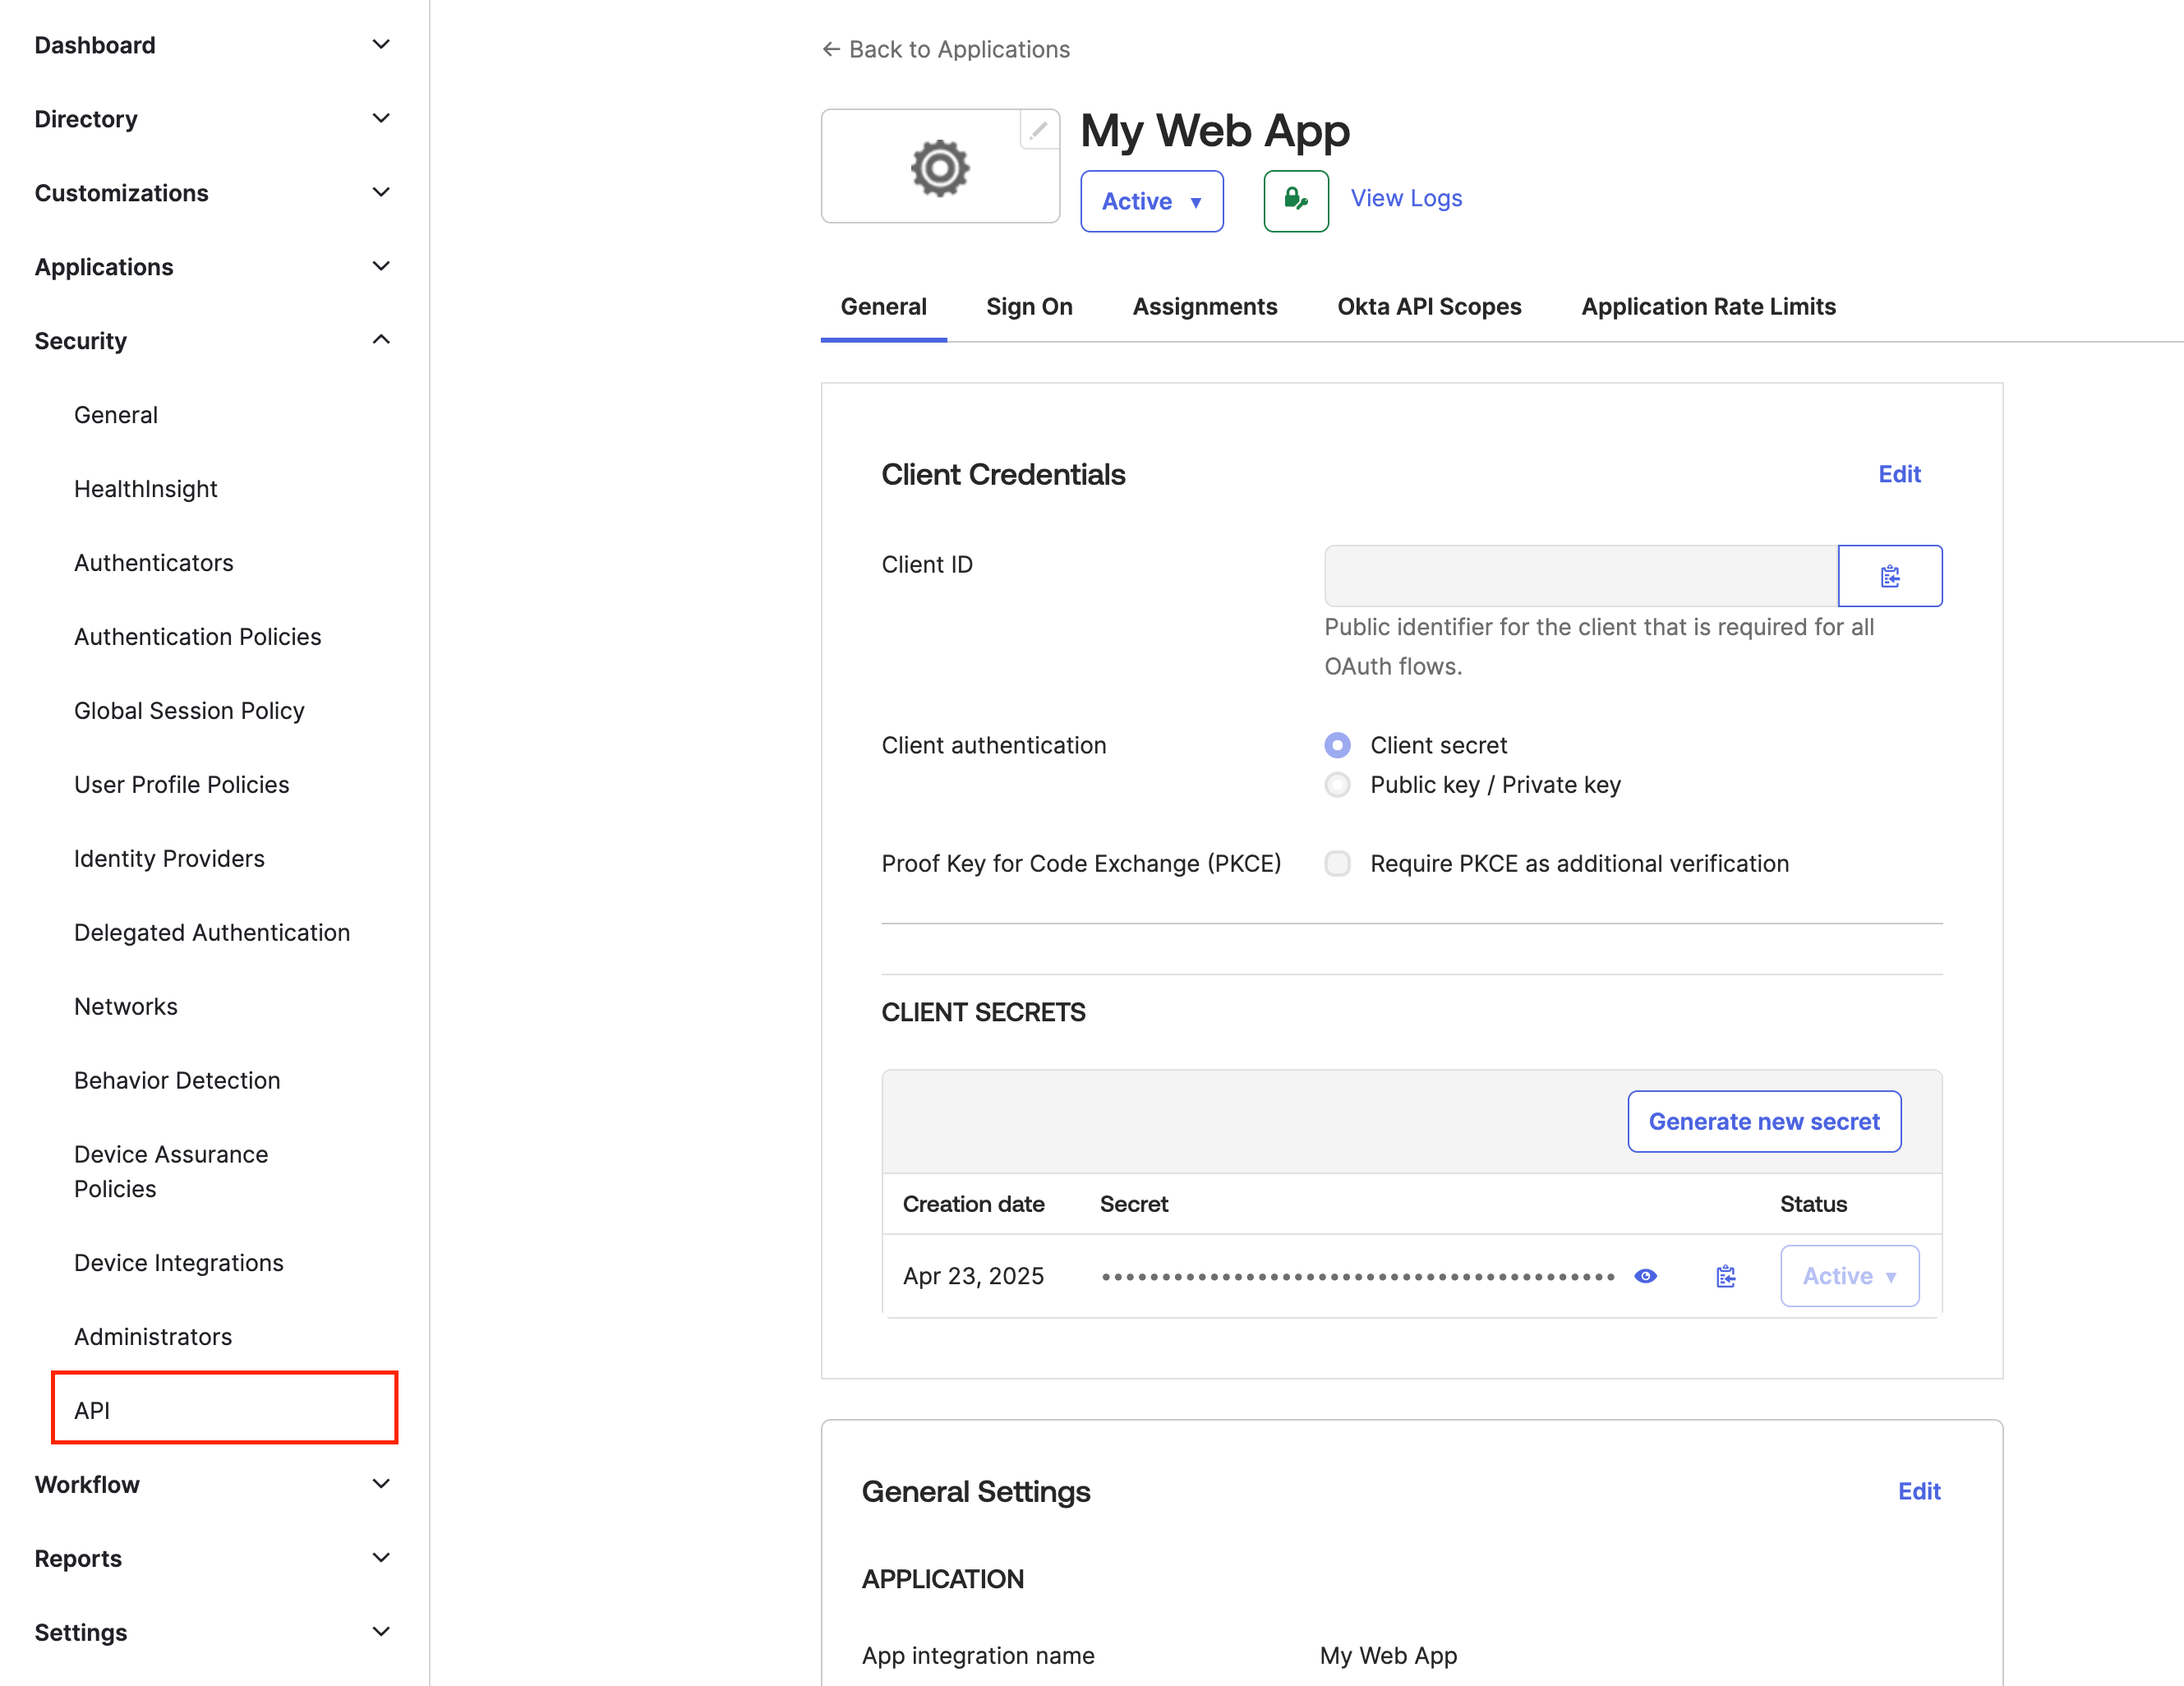
    Navigate to **Security** -> **API**.

    <Frame>
      <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/edit-client-credentials-for-web-app.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=5b1b11956c408b77b3be055427f601e7" alt="Client Credentials section editing client ID and authentication settings" title="Edit client credentials for web app" width="2658" height="2052" data-path="images/studio/sso/edit-client-credentials-for-web-app.png" />
    </Frame>
  </Step>

  <Step>
    Select the **default** authorization server.
  </Step>

  <Step>
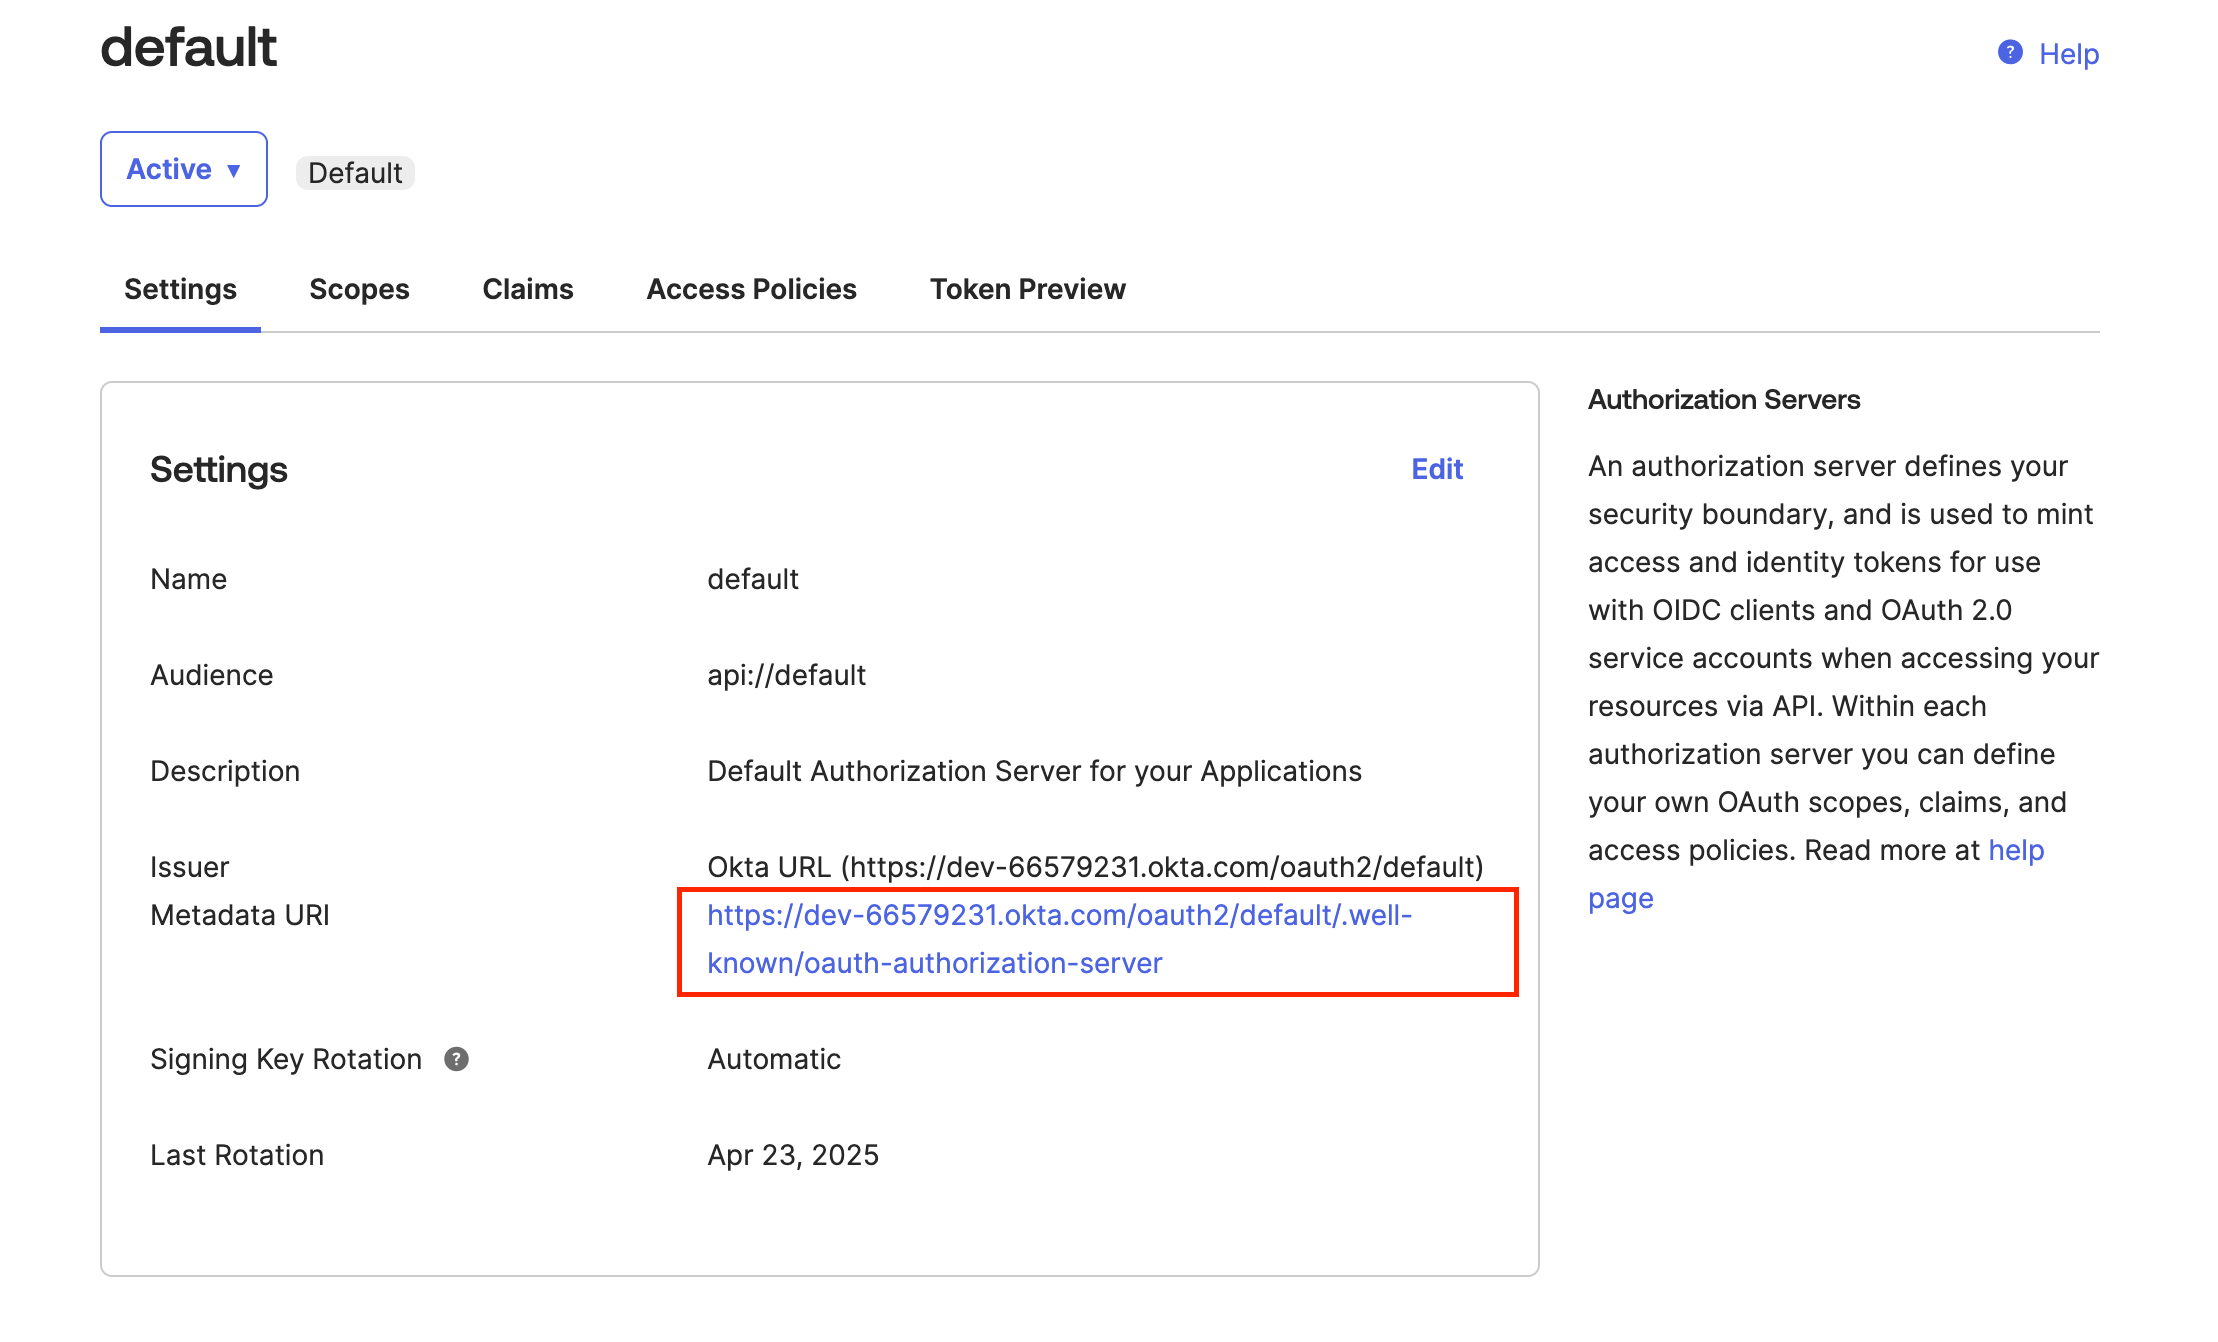
    Copy the **Metadata URI.**

    <Frame>
      <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/default-authorization-server-metadata.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=803c9ce981038f6e7847a141a687dfa6" alt="Default authorization server settings highlighting metadata URI in Cosmo Docs" title="Default authorization server metadata" width="2218" height="1342" data-path="images/studio/sso/default-authorization-server-metadata.png" />
    </Frame>
  </Step>

  <Step>
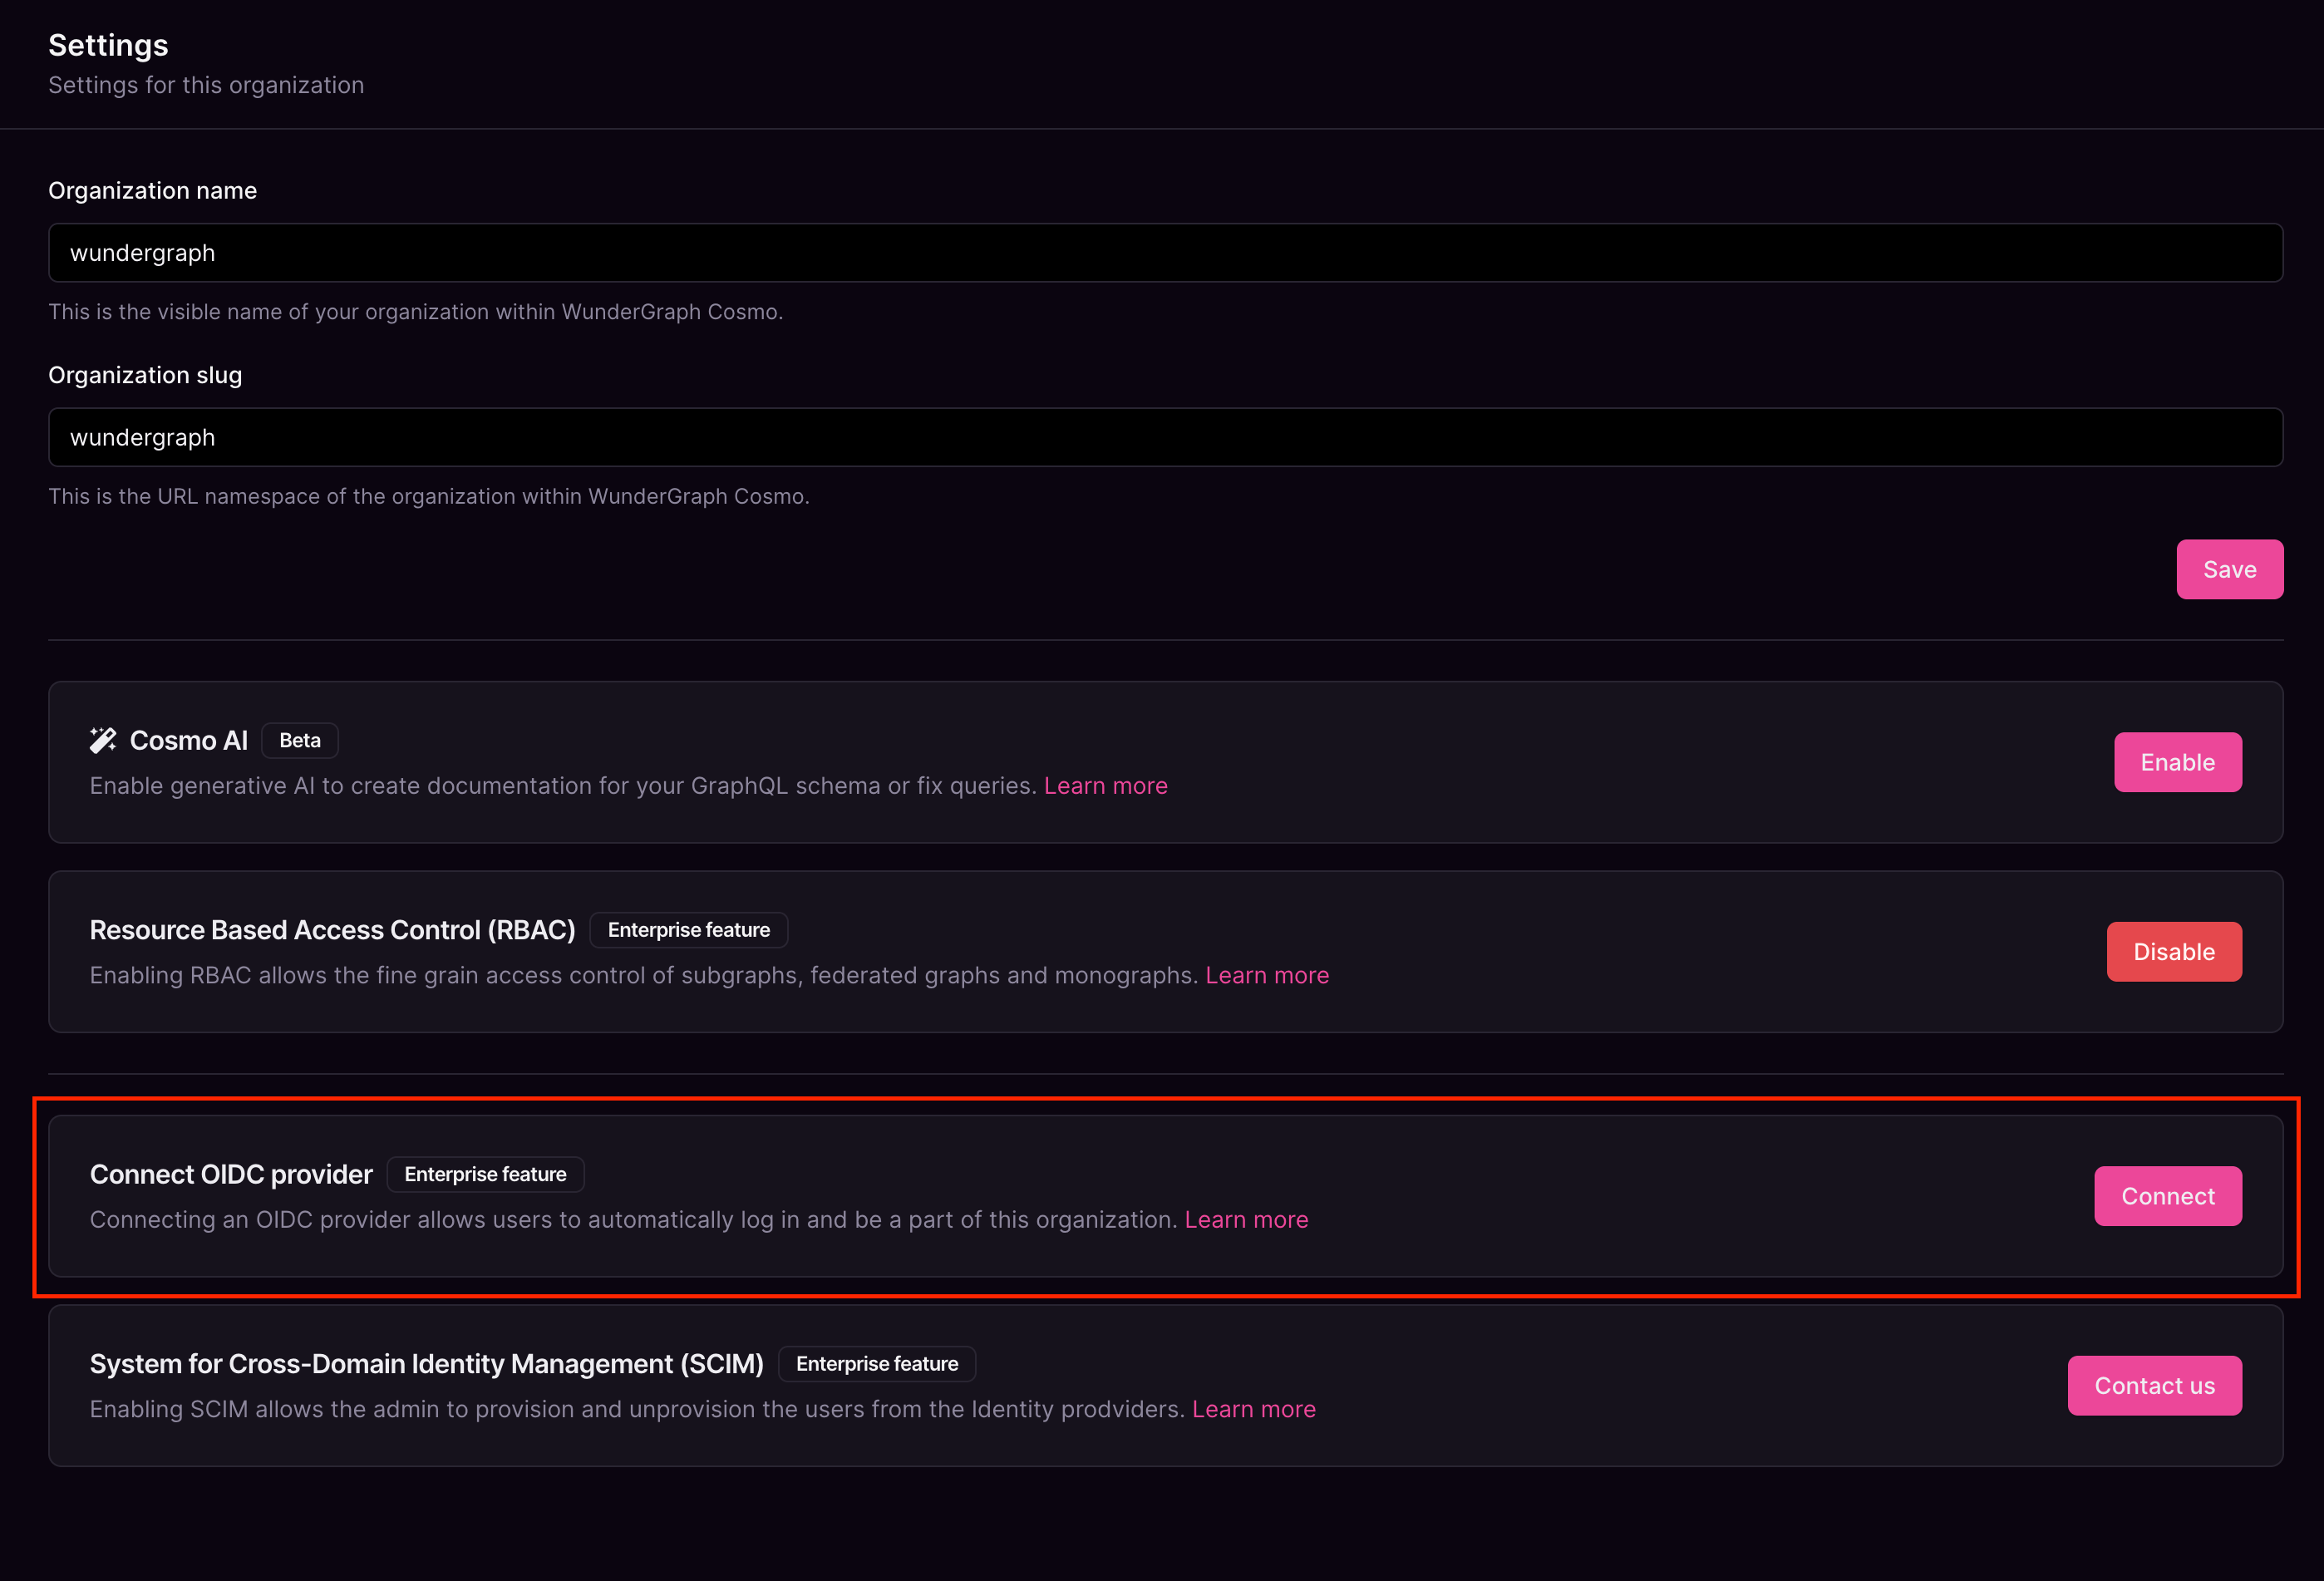
    Navigate to the settings page on Cosmo.
    <Frame>
      <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/organization-settings-with-ai-rbac-scim.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=8419d4c3f28278891d5d2d53dad2fa0f" alt="Organization settings showing name, slug, and status of AI, RBAC, and SCIM features" title="Organization settings with AI, RBAC, SCIM" width="2796" height="1902" data-path="images/studio/sso/organization-settings-with-ai-rbac-scim.png" />
    </Frame>
  </Step>

  <Step>
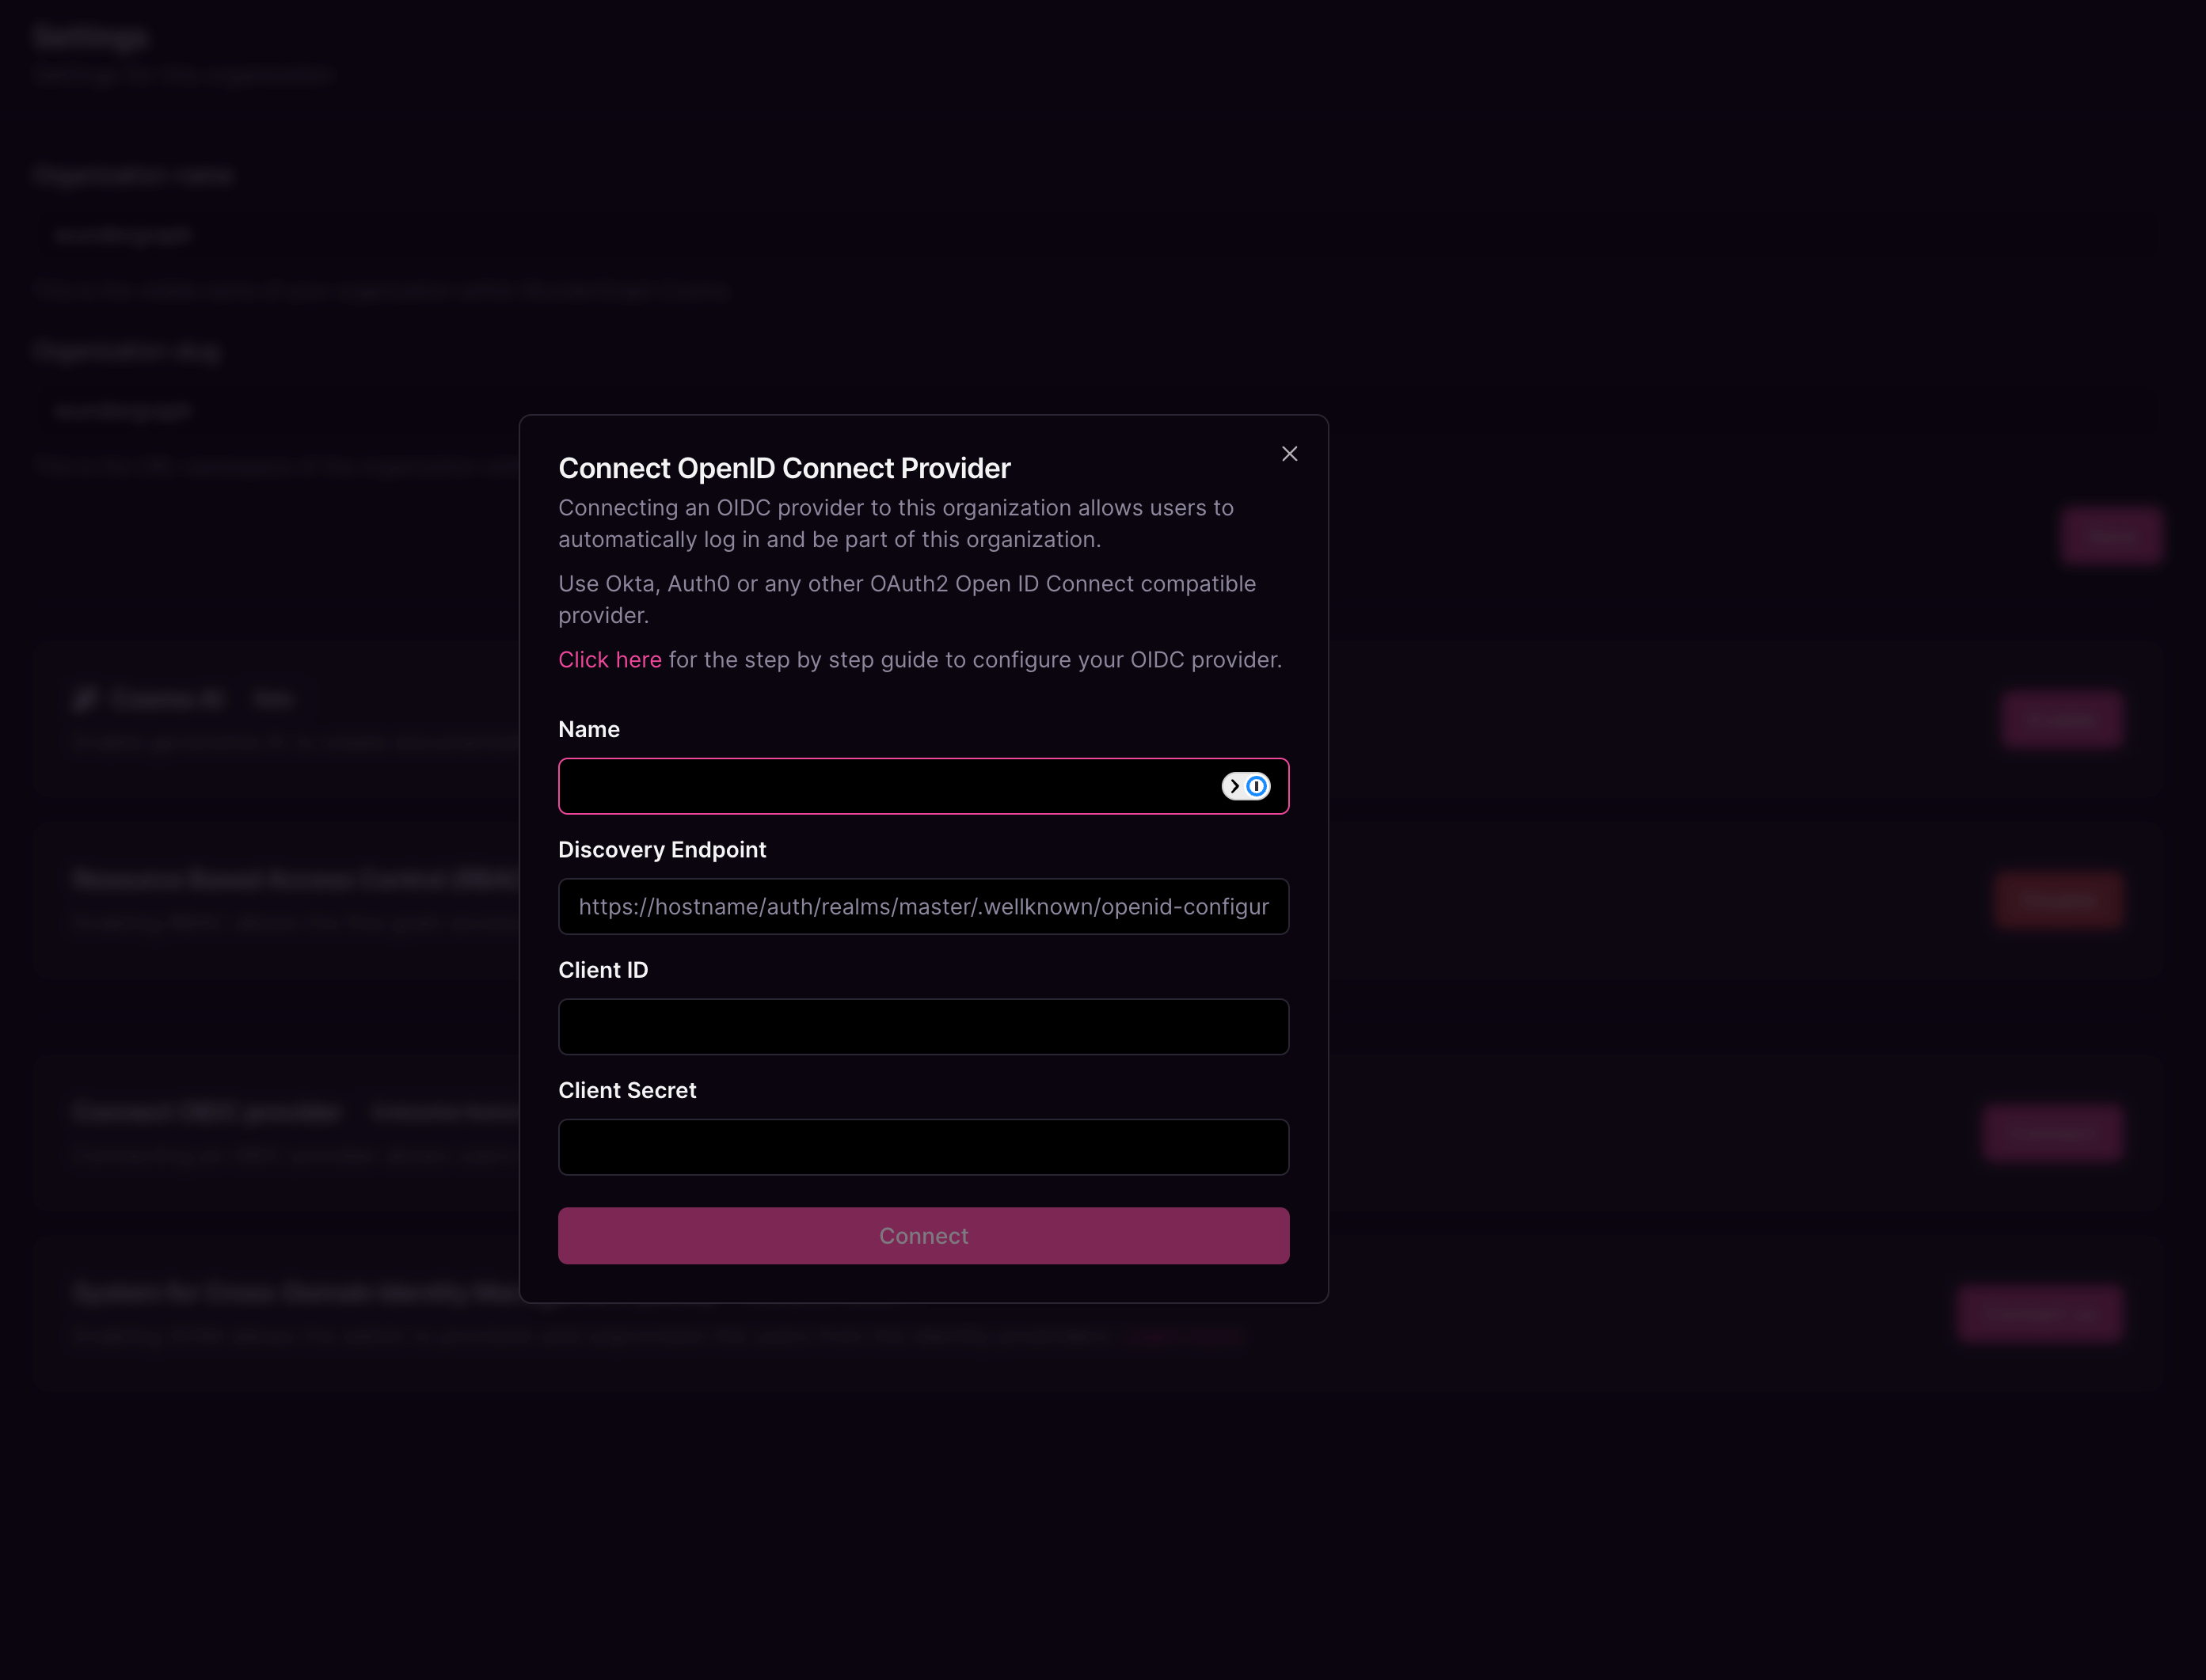
    Give the connection a name, paste the **Metadata URI** copied before, into the  **Discovery Endpoint,**and paste the **Client ID** and  **Client secret** copied before into the **Client ID** and  **Client Secret fields respectively,**and then click on **Connect.**
    <Frame>
      <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/oidc-provider-configuration-form.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=b3edc73033256a7ad5dd6a5bb737bf1b" alt="Connect OpenID Connect Provider form with fields for name, endpoint, and credentials" title="OIDC provider configuration form" width="2786" height="2122" data-path="images/studio/sso/oidc-provider-configuration-form.png" />
    </Frame>
  </Step>

  <Step>
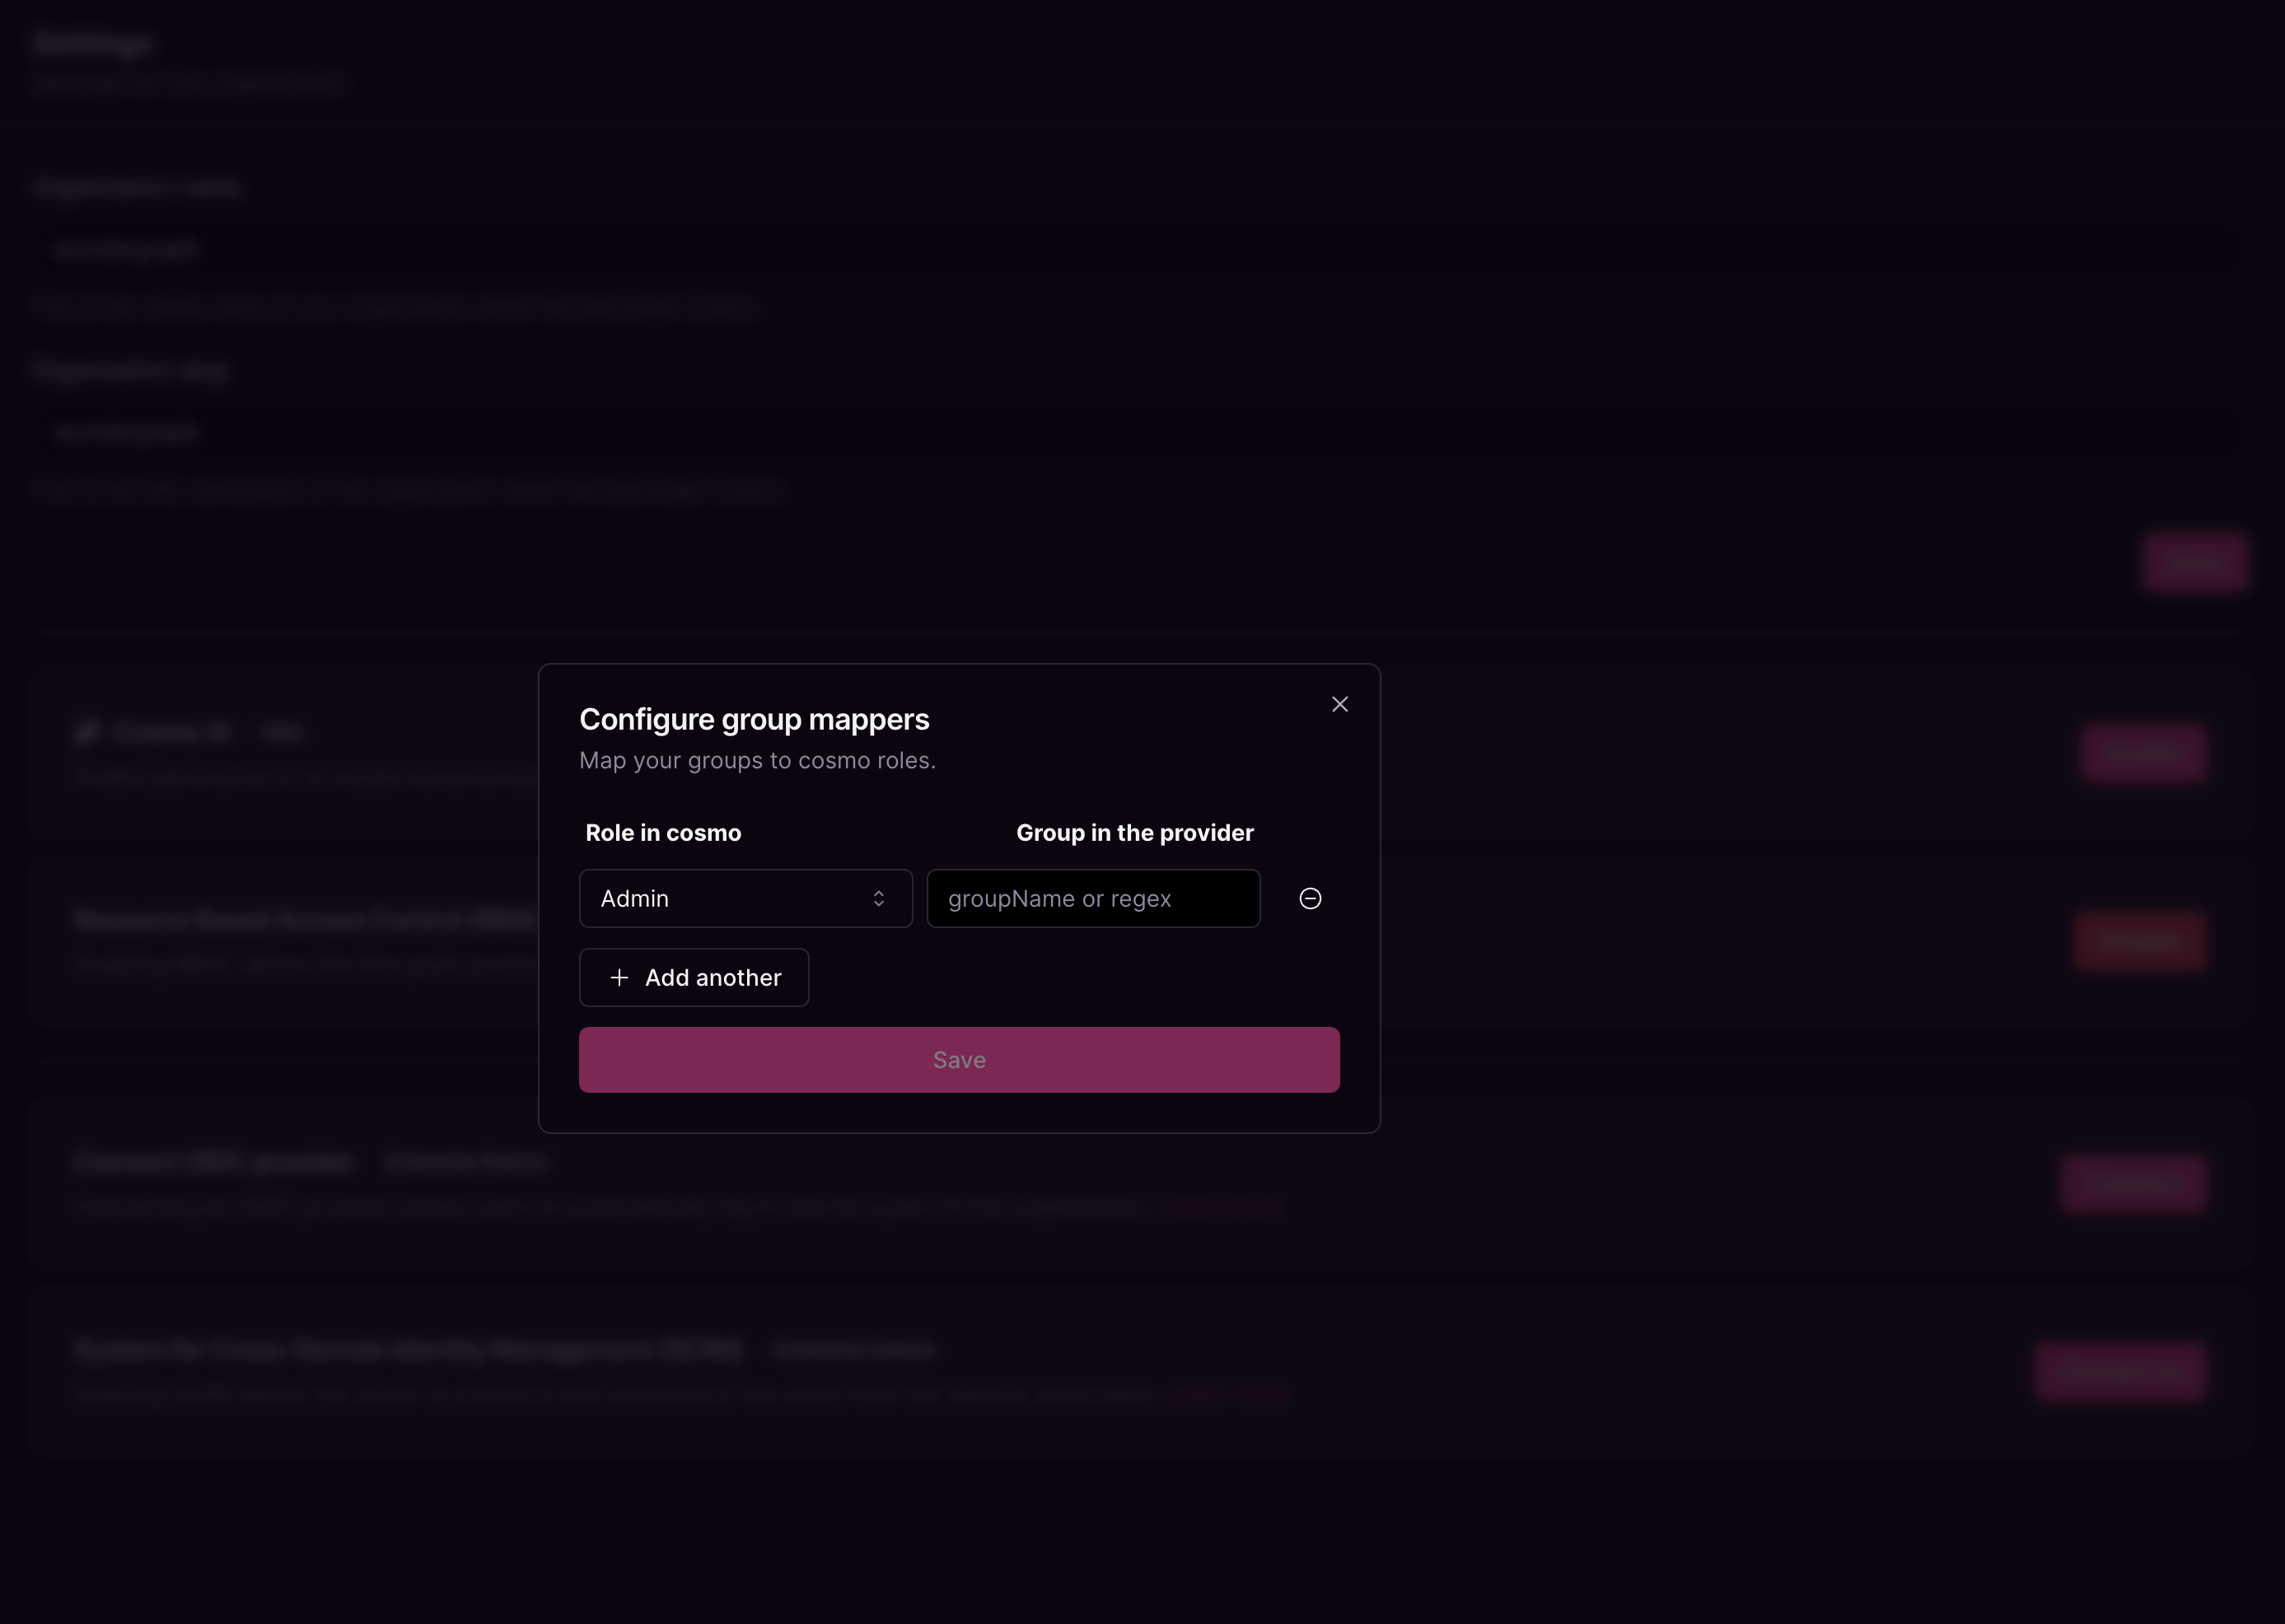
    Configure the mapping between the roles in Cosmo and the user groups in Okta. The field **Group in the provider** can be populated with the name of the group or a regex to match the user groups. Once all the mappers are configured, click on **Save**.
    <Frame>
      <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/group-to-role-mapping-dialog.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=db2ab7b71d268fcf0f13021371874333" alt="Group mapper configuration dialog linking provider groups to Cosmo roles" title="Group-to-role mapping dialog" width="2774" height="1972" data-path="images/studio/sso/group-to-role-mapping-dialog.png" />
    </Frame>
  </Step>

  <Step>
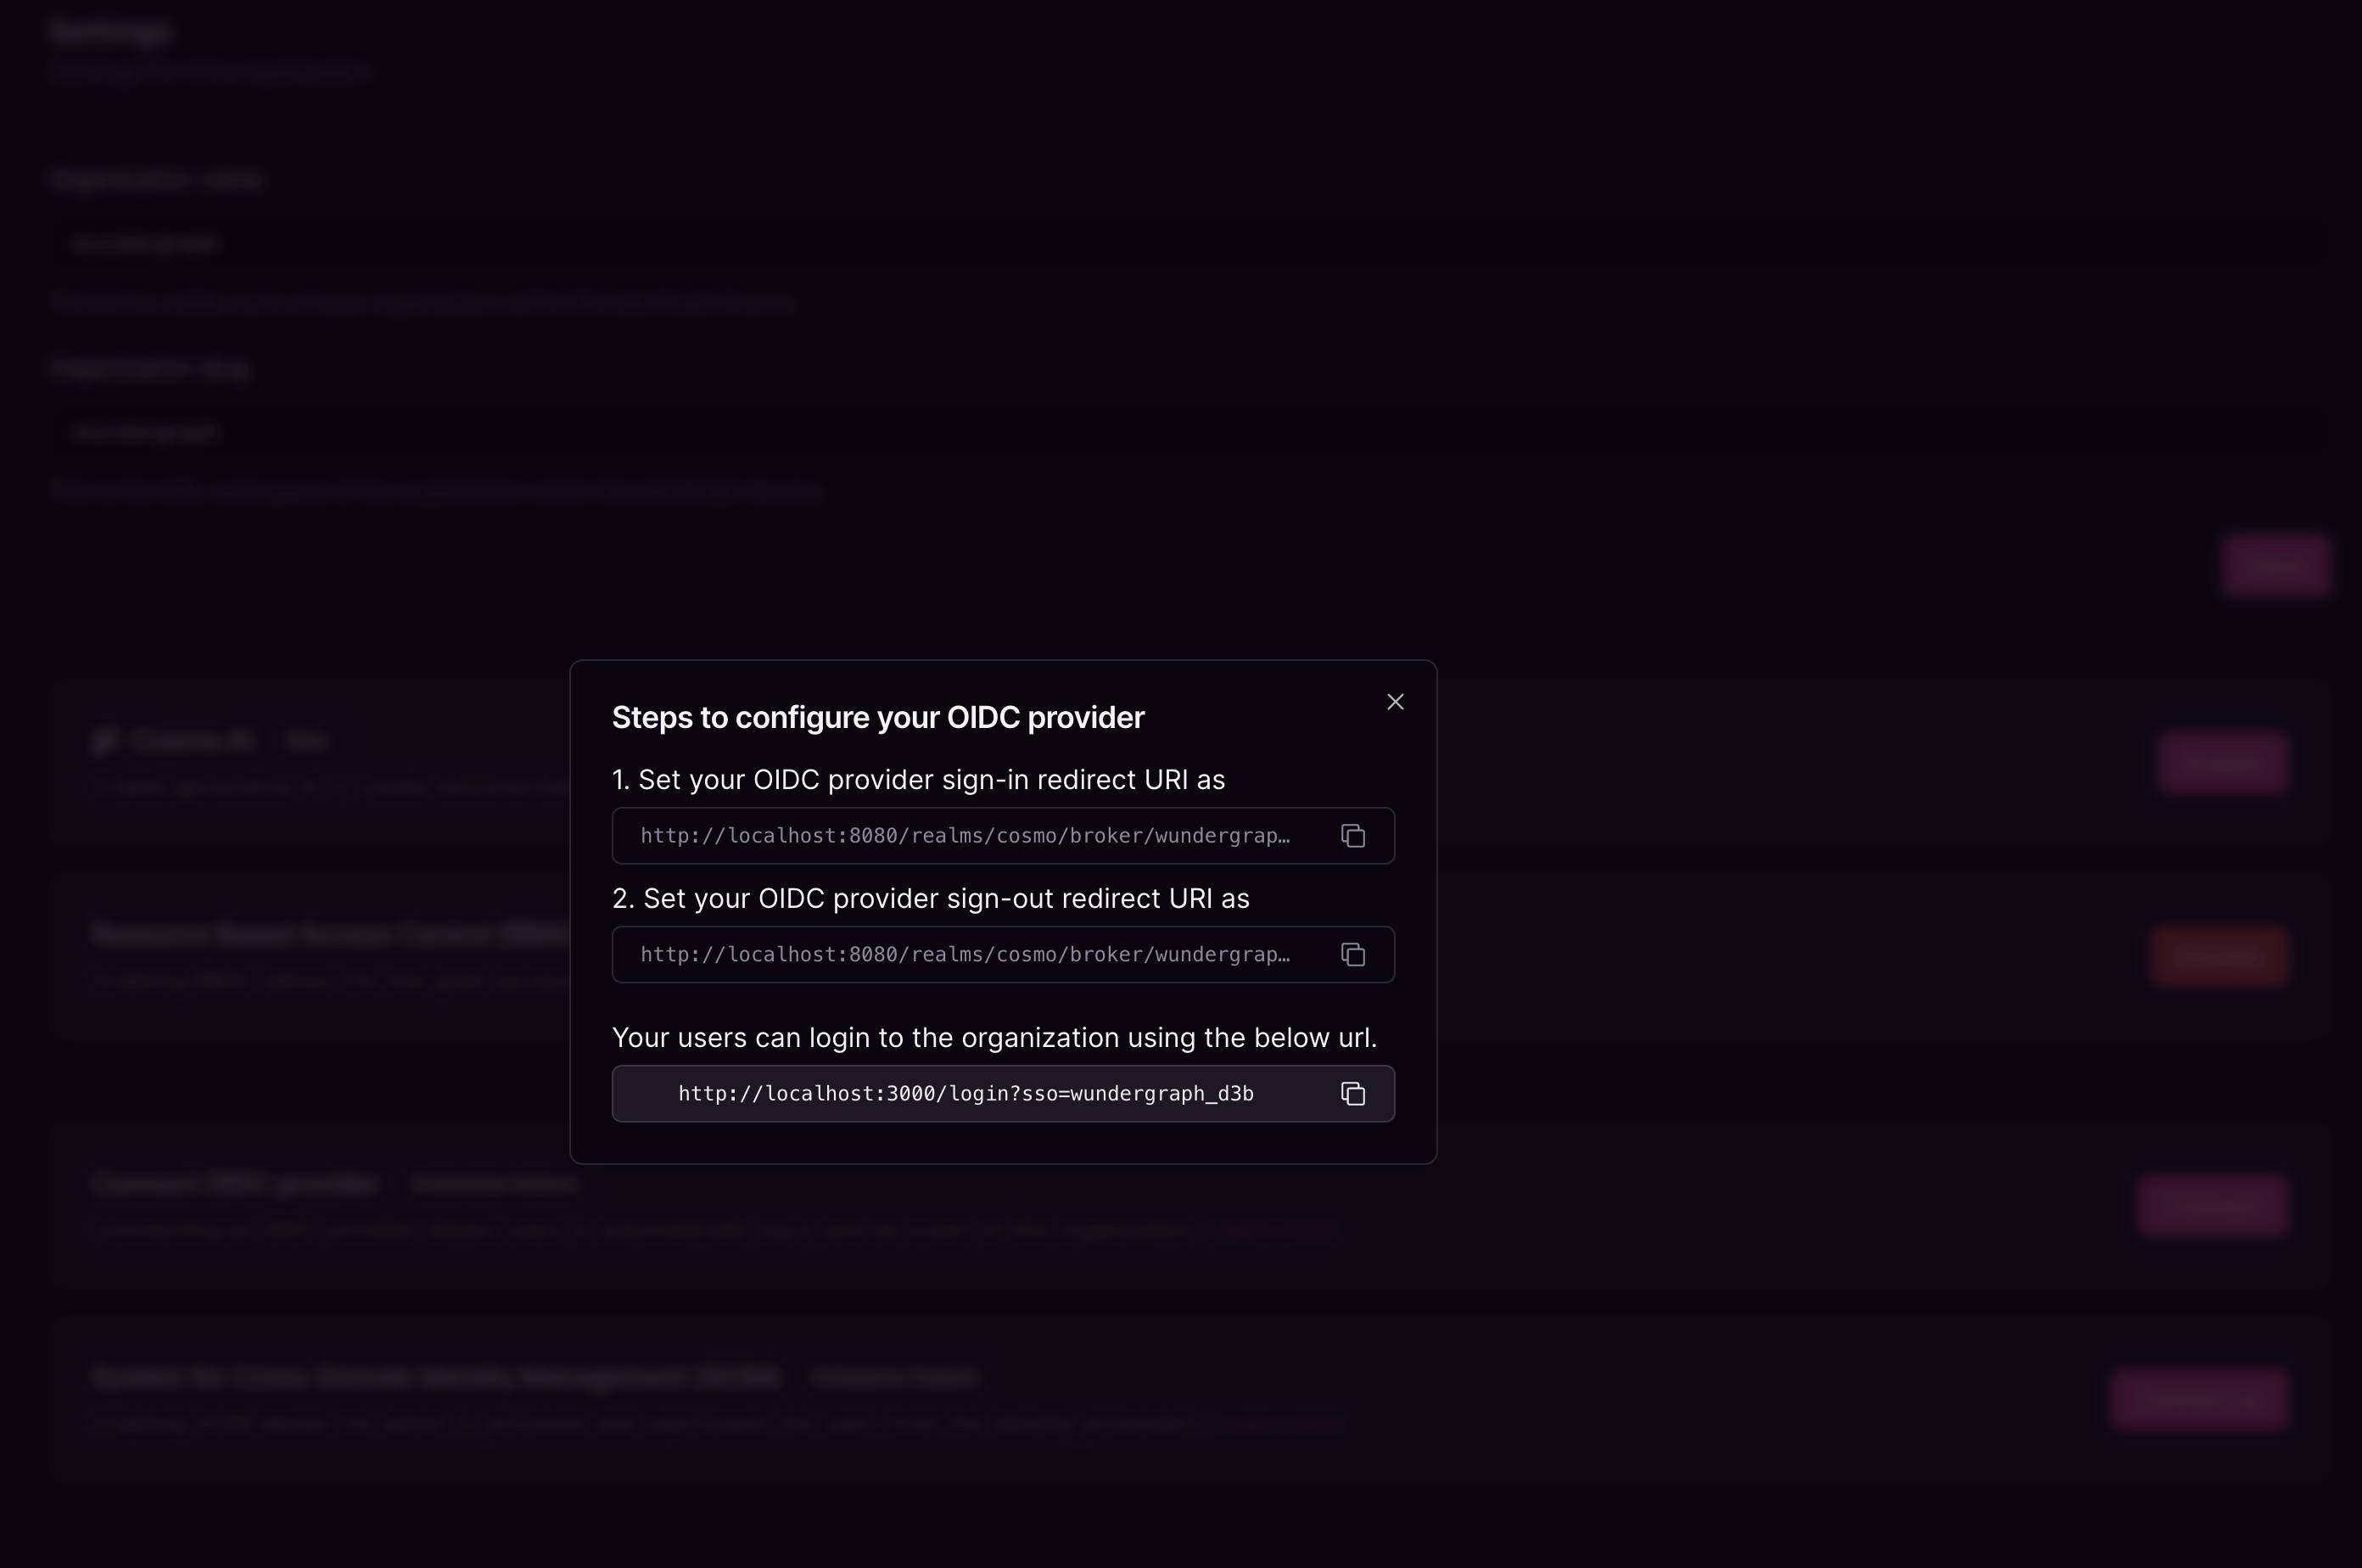
    Copy the sign-in and sign-out redirect URIs displayed in the dialog.
    <Frame>
      <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/oidc-provider-configuration-steps.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=772d1eaf2a4f84bbe18115e821b6dfe8" alt="Steps to configure OIDC provider with sign-in and sign-out redirect URLs" title="OIDC provider configuration steps" width="2784" height="1848" data-path="images/studio/sso/oidc-provider-configuration-steps.png" />
    </Frame>
  </Step>

  <Step>
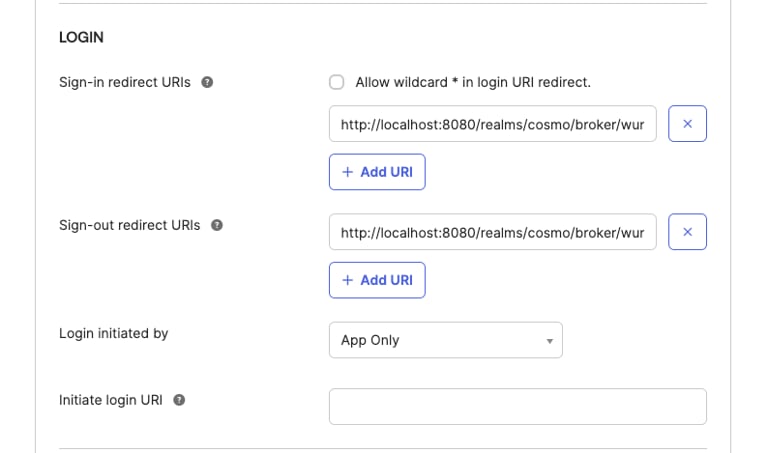
    Navigate back to the application created on Okta and populate the Sign-in and Sign-out redirect URIs with the above-copied values. Click on **Save**.
    <Frame>
      <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/login-configuration-with-redirect-urls.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=48105ed131facc18bb87c787aad78ece" alt="Login configuration specifying sign-in and sign-out redirect URIs and login initiator" title="Login configuration with redirect URLs" width="768" height="453" data-path="images/studio/sso/login-configuration-with-redirect-urls.png" />
    </Frame>
  </Step>

  <Step>
    Depending on your Okta tenant's available features, configure the `ssoGroups` claim directly on your application, using either <a href="#using-authorization-servers">Authorization Servers</a> or <a href="#using-token-claims">Token Claims</a>.
  </Step>

  <Step>
    You may now assign users and groups to the application. Assigned users can sign in to Cosmo with the provider URL.
  </Step>
</Steps>

<Info>
  Users assigned to the application must have a username.
</Info>

### Using Authorization Servers

<Step>
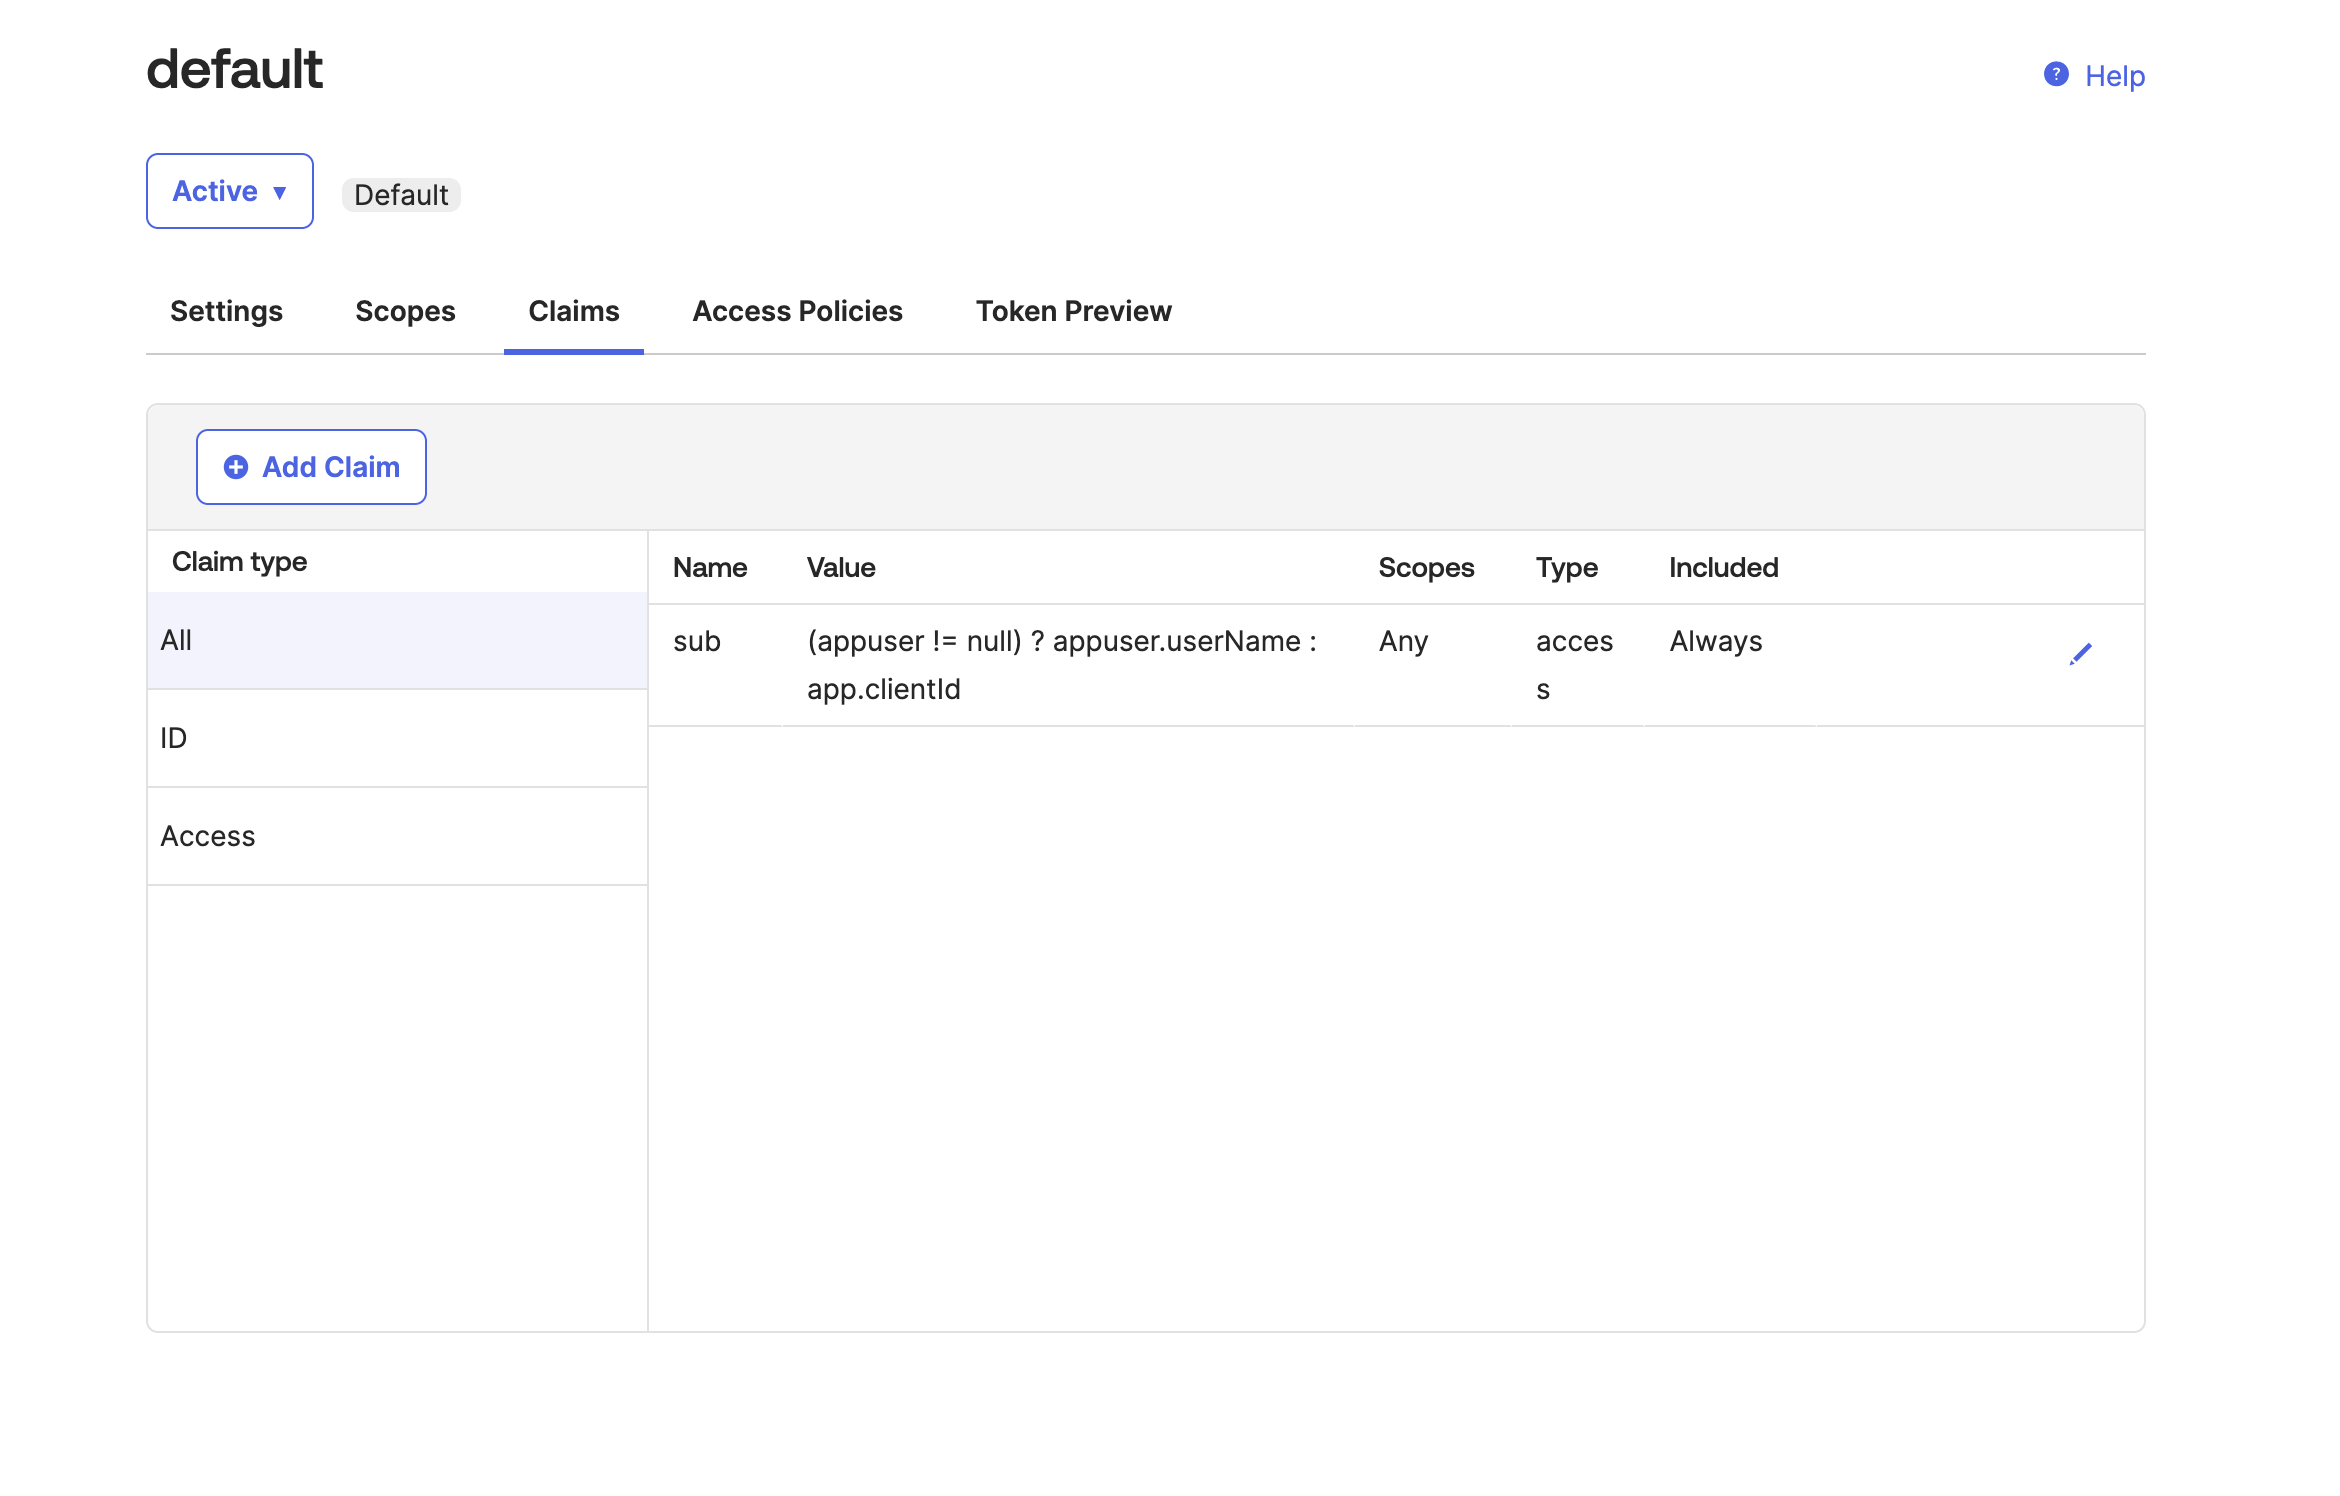
  Navigate to Security → API, then click the **Default authorization server**. Open the Claims tab, then click **Add Claim**.
  <Frame>
    <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/access-policies-with-token-preview.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=3303e96992ac0a8231b061317772a516" alt="Access Policies section showing claims list and Token Preview button" title="Access Policies with Token Preview" width="2340" height="1496" data-path="images/studio/sso/access-policies-with-token-preview.png" />
  </Frame>
</Step>

<Step>
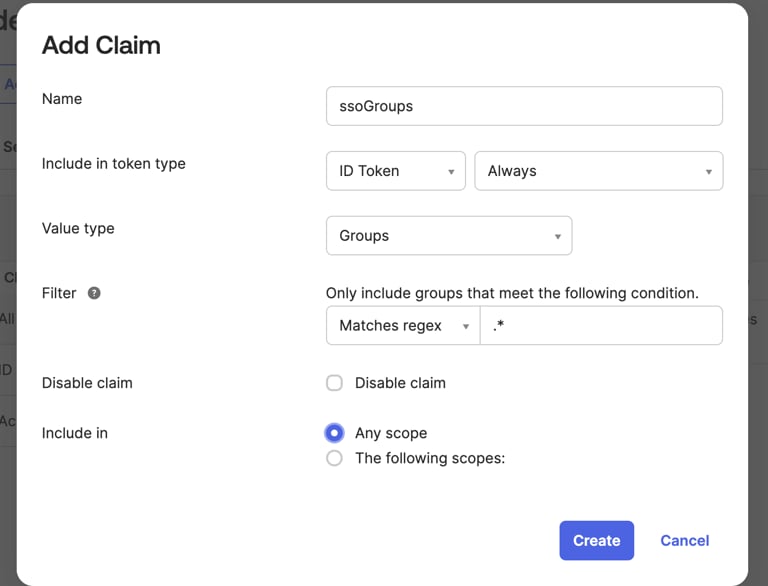
  Name the claim `ssoGroups` and include it in the **ID Token**. For value type, select **Groups**. For filter, select **Matches** regex and enter `.*` in the field. Click **Create**.
  <Frame>
    <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/add-claim-dialog-for-group-filters.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=6ecd441b27c4724cf7760a05d41cf1f1" alt="Add Claim dialog for ssoGroups with filters, scopes, and create button" title="Add Claim dialog for group filters" width="768" height="586" data-path="images/studio/sso/add-claim-dialog-for-group-filters.png" />
  </Frame>
</Step>

### Using Token Claims

<Step>
  Navigate to Applications and Resources → Applications, then select the application.
</Step>

<Step>
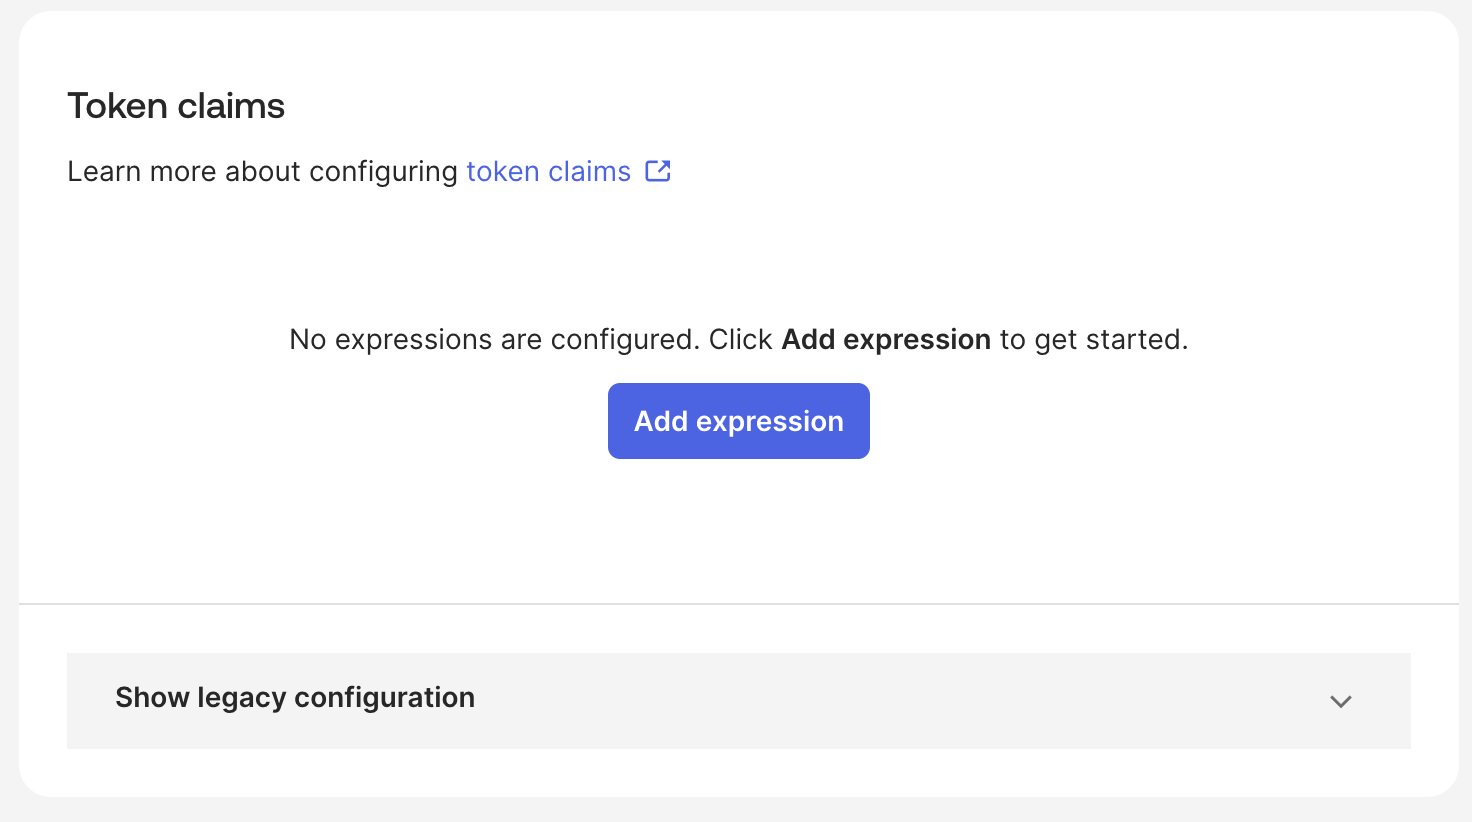
  Select the `Sign On` tab, scroll to the `Token Claims` card, then click **Add Expression**.
  <Frame>
    <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/okta-token-claims-card.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=52febee865bb6073db291cde6719aec9" alt="Access the Token claims under the application Sign On configuration" title="Access Token claims under the sign on configuration" width="1472" height="822" data-path="images/studio/sso/okta-token-claims-card.png" />
  </Frame>
</Step>

<Step>
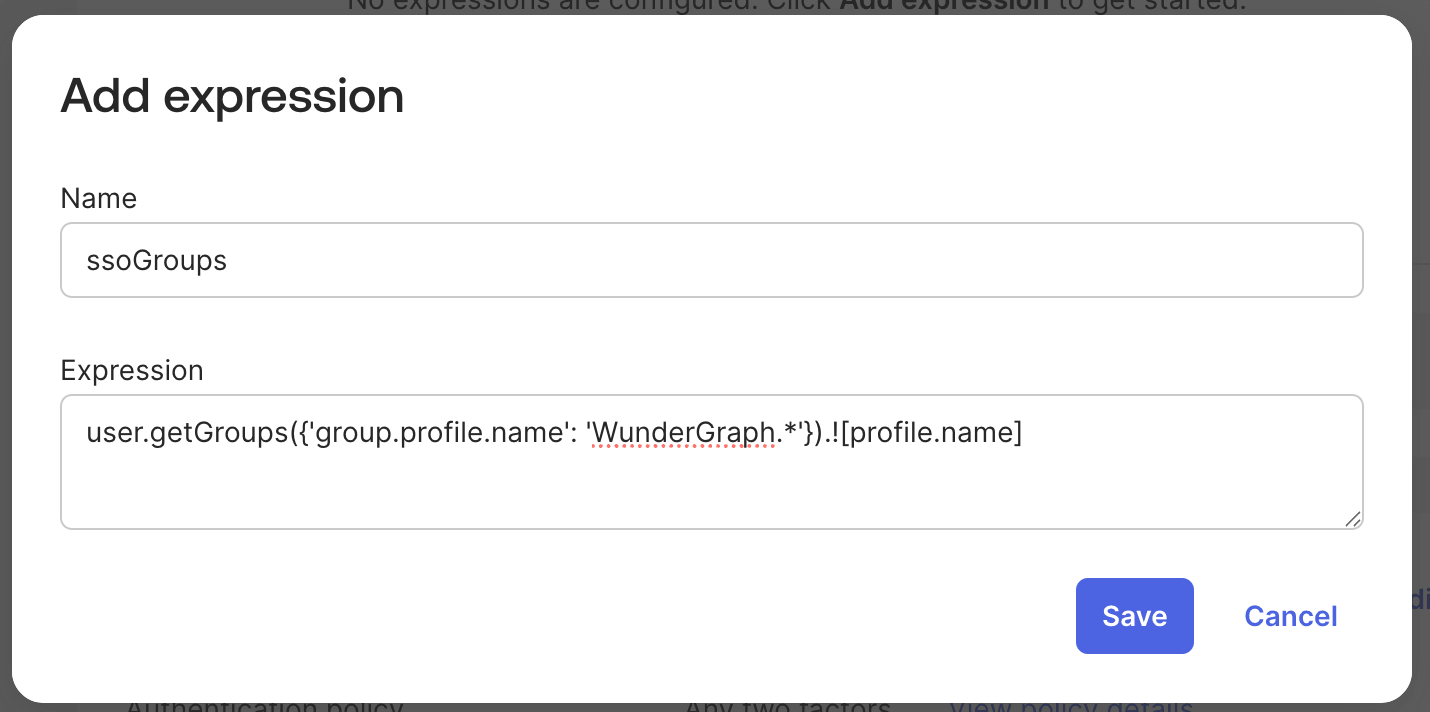
  Name the expression `ssoGroups`. For the expression, enter `user.getGroups({'group.profile.name': 'WunderGraph.*'}).![profile.name]`, then click **Save**.

  This expression tells Okta to assign all groups that start with `WunderGraph` to the `ssoGroups` claim. You can adjust the expression to fit your organization's needs. To learn more,
  refer to the <a href="https://help.okta.com/oie/en-us/content/topics/apps/federated-claims-overview.htm" target="_blank" rel="noopener noreferrer">Okta documentation</a>.

  <Frame>
    <img src="https://mintcdn.com/wundergraphinc-milinda-eng-9918-router-cache-tag-based-inva/l8RJPXDEie4WukjB/images/studio/sso/add-token-claim-expression-dialog.png?fit=max&auto=format&n=l8RJPXDEie4WukjB&q=85&s=851662330ef91e00fade05b9e6508112" alt="Add claim expression dialog for ssoGroups" title="Add claim expression dialog" width="1430" height="712" data-path="images/studio/sso/add-token-claim-expression-dialog.png" />
  </Frame>
</Step>